Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 32 of 110
curl Patches HTTP/2 Upload Flaw After PoC Demonstrates Client-Side Code Execution Important The Hacker News
2026-10-14 The Hacker News

curl Patches HTTP/2 Upload Flaw After PoC Demonstrates Client-Side Code Execution

A flaw in how curl handles HTTP/2 uploads lets a malicious server receiving an upload corrupt the client's memory, and the researcher who reported it turned that into code execution on the uploading machine. The curl project fixed it on October 14 in curl 8.23.0. Taking over a client needs exact knowledge of its build and memory layout, and curl expects a re…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How to Run a Deepfake Readiness Drill Before a Cloned Voice Calls Your Team Moderate The Hacker News
2026-10-14 The Hacker News

How to Run a Deepfake Readiness Drill Before a Cloned Voice Calls Your Team

Cloned voices and synthetic video calls now show up in payment fraud, help desk resets, and access requests. A structured drill shows security teams exactly where verification breaks down, while nothing is at stake. The call comes in at 4:40 on a Friday. It's the CFO, or it sounds exactly like her, asking the controller to push a supplier payment out before …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Hirudo Android malware replaces banking apps to evade security checks Important BleepingComputer
2026-10-14 BleepingComputer

Hirudo Android malware replaces banking apps to evade security checks

A new Android malware called Hirudo steals bank account credentials by replacing legitimate banking apps with modified versions that disable security checks. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hidden Audio Recorder Found at OpenAI as Employee Faces Federal Charges Moderate SecurityAffairs
2026-10-14 SecurityAffairs

Hidden Audio Recorder Found at OpenAI as Employee Faces Federal Charges

OpenAI employee charged with planting hidden audio recorders to capture sensitive discussions about AI research and company strategy. On September 30, OpenAI staff found a small audio recording device jammed into a USB port on the back of a television in an executive conference room in their San Francisco office. The device had been there since September 28,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Update Windows: Record Patch Tuesday fixes flaw already under attack Critical CVE-2026-96951 Malwarebytes Labs
2026-10-14 Malwarebytes Labs

Update Windows: Record Patch Tuesday fixes flaw already under attack

Microsoft’s October Patch Tuesday release addresses a record-breaking 1,413 vulnerabilities , including an actively exploited Windows Shell zero-day and two other publicly disclosed flaws. Just when you thought a previous record would stand for a while, Microsoft comes out again with the largest monthly Patch Tuesday release. Microsoft has said its growing u…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Researchers Used a Public OpenAI Model to Build a $250,000 Chrome Full-Chain Exploit in Six Days Important The Hacker News
2026-10-14 The Hacker News

Researchers Used a Public OpenAI Model to Build a $250,000 Chrome Full-Chain Exploit in Six Days

A team at security firm XBOW chained three then-unknown Google Chrome bugs into a single attack that runs code on a Windows computer when the user only loads a web page, the company said. Its researchers built the attack in six days by directing AI agents running OpenAI's publicly available GPT-5.6 Sol model. Google has since confirmed all three bugs, fixed …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
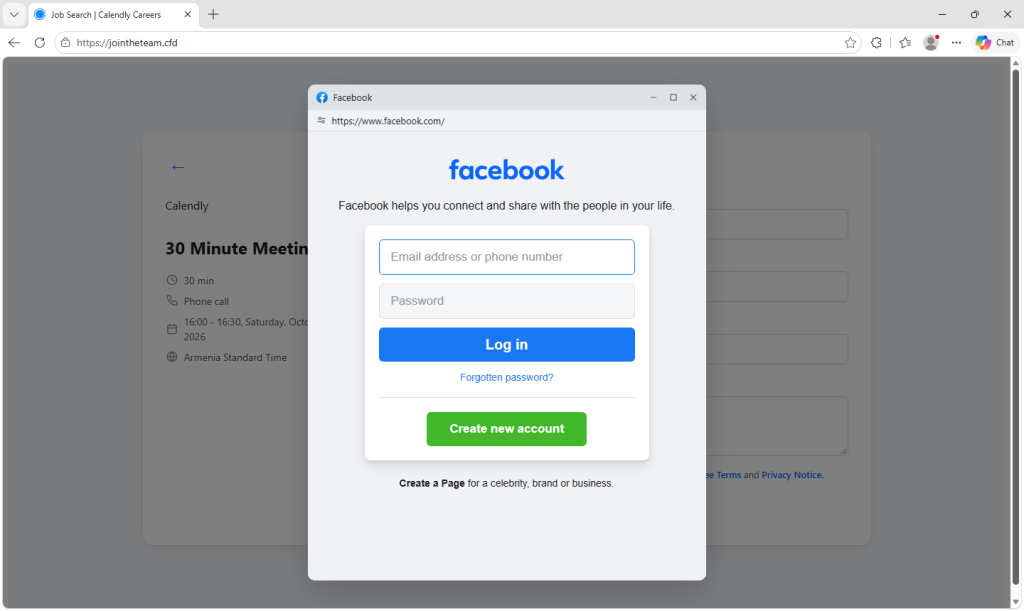
Fake Calendly “Meta Careers” pages steal Facebook and Google logins Moderate Malwarebytes Labs
2026-10-14 Malwarebytes Labs

Fake Calendly “Meta Careers” pages steal Facebook and Google logins

We found a wave of websites posing as Calendly booking pages for job interviews at Meta. Visitors pick a slot for a 30-minute phone call with a recruiter, fill in their details, and pass what looks like a CAPTCHA. Then the page asks them to log in to Facebook. The interview is fake. The pages are designed to steal the visitor’s Facebook login details, includ…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hirudo Android Trojan Uses Patched Banking Apps to Bypass Their Built-In Security Checks Important The Hacker News
2026-10-14 The Hacker News

Hirudo Android Trojan Uses Patched Banking Apps to Bypass Their Built-In Security Checks

Cybersecurity researchers have disclosed details of a new Android banking trojan called Hirudo that works by replacing legitimate banking apps with purpose-built patched versions designed to bypass security checks from inside the app itself, marking a new escalation in financial fraud. Dutch mobile security company ThreatFabric said it identified replacement…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
An AI Agent Found a Critical OTP Bypass in Production. The Attack Was the Easy Part. Critical The Hacker News
2026-10-14 The Hacker News

An AI Agent Found a Critical OTP Bypass in Production. The Attack Was the Easy Part.

The bug was simple: the login let you choose where your sign-in code went. Proving it on a live website was the hard part. TL;DR During an authorized assessment, an AI pentesting agent found a critical authentication bypass on a major insurer's production website, on its own. One login request let the user choose where the one-time passcode went. The attack …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Phase Eight, Hobbs and Whistles owner joins growing list of fashion retailers targeted by hackers Important Help Net Security
2026-10-14 Help Net Security

Phase Eight, Hobbs and Whistles owner joins growing list of fashion retailers targeted by hackers

People who have shopped with Phase Eight, Hobbs or Whistles will have to wait to find out whether their personal information was exposed in a cyberattack on the company behind the three UK fashion brands. TFG London, the UK business of South African retail group The Foschini Group (TFG), detected the incident on Sunday, 11 October 2026. In a statement releas…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft: Recent Windows updates may trigger Remote Desktop failures Moderate BleepingComputer
2026-10-14 BleepingComputer

Microsoft: Recent Windows updates may trigger Remote Desktop failures

Microsoft has confirmed that non-admin users may be unable to connect to devices via Remote Desktop after installing recent Windows updates if the "Administrator protection" security feature is enabled. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Police receive fake murder tip from Anthropic’s Claude AI Moderate Malwarebytes Labs
2026-10-14 Malwarebytes Labs

Police receive fake murder tip from Anthropic’s Claude AI

Police tip hotlines already have their fair share of crank callers. Apparently they now have to contend with crank AI agents as well. AI agents have already been caught hacking software companies , breaching an Australian government portal , and trying to hack a Canadian government website . Now Anthropic’s Claude has added a made-up murder tip to the list. …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Radware MCP Server Protection monitors agent activity and guards against protocol abuse Moderate Help Net Security
2026-10-14 Help Net Security

Radware MCP Server Protection monitors agent activity and guards against protocol abuse

Radware has announced Radware Model Context Protocol (MCP) Server Protection, a purpose-built solution designed to help organizations more securely adopt MCP as AI agents gain greater access to enterprise applications, data and business workflows. The solution is intended to give organizations visibility into their MCP infrastructure, help protect MCP server…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
SolarWinds Avior pairs IT automation with human approval and audit trails Moderate Help Net Security
2026-10-14 Help Net Security

SolarWinds Avior pairs IT automation with human approval and audit trails

SolarWinds has announced the launch of Avior, a standalone, goal-oriented agentic AI system purpose-built for mission-critical IT environments. Built on the SolarWinds Platform, Avior will help IT teams securely define goals, coordinate specialized agents, and track progress toward measurable outcomes across hybrid digital ecosystems. As technology infrastru…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Chainguard Harness uses frontier AI to test running applications for vulnerabilities Important Help Net Security
2026-10-14 Help Net Security

Chainguard Harness uses frontier AI to test running applications for vulnerabilities

Chainguard has announced Chainguard Harness, a new cyber harness that uses frontier AI models like Anthropic’s Claude Mythos 5.1 to find and fix exploitable vulnerabilities in an organization’s application code. Harness builds an application from an organization’s source code in an isolated microVM, instructs a frontier model to hunt for exploitable vulnerab…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Volexity Uncovers Stealthy Ivanti VPN Attack Using Three Zero-Day Vulnerabilities Critical CVE-2026-104935 SecurityAffairs
2026-10-14 SecurityAffairs

Volexity Uncovers Stealthy Ivanti VPN Attack Using Three Zero-Day Vulnerabilities

Ivanti VPN zero-days let attackers gain root access, steal credentials, evade detection, and prepare for wider network compromise. On October 5, Volexity started investigating suspicious activity at one of its monitoring customers and traced everything back to an Ivanti Connect Secure VPN appliance running version 22.8R2.4, the latest build available at the …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Scytale MCP gives AI tools scoped, read-only access to compliance data Moderate Help Net Security
2026-10-14 Help Net Security

Scytale MCP gives AI tools scoped, read-only access to compliance data

Scytale has announced the launch of Scytale MCP, a Model Context Protocol server that connects a customer’s AI tools directly to their compliance program. With Scytale MCP, tools such as Claude and ChatGPT can query live compliance data and complete routine work through plain language instead of screen-by-screen navigation. The release reflects how AI-native…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

GitHub adopts cheaper AI model to catch secrets developers leave in code Moderate Help Net Security
2026-10-14 Help Net Security

GitHub adopts cheaper AI model to catch secrets developers leave in code

GitHub has trained a credential classifier to improve generic secret detection and reduce false alerts. The new pipeline cut median post-push scan execution time by 86% and model serving costs by more than 98% compared with its previous large language model (LLM) pipeline. GitHub’s secret scanning covers two stages of development. Push protection checks chan…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Attackers chained three Ivanti zero-days to gain root on fully patched VPN appliances Critical Help Net Security
2026-10-14 Help Net Security

Attackers chained three Ivanti zero-days to gain root on fully patched VPN appliances

A threat actor has been using an exploit chain combining three vulnerabilities in Ivanti’s Connect Secure (ICS) appliances to breach organizations, collect credentials, exfiltrate configuration data, and perform network reconnaissance. “In the first week of October 2026, Volexity discovered an unknown threat actor, UTA0576, abusing a zero-day exploit chain t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI engineer arrested for allegedly trying to eavesdrop on executive meetings Moderate Help Net Security
2026-10-14 Help Net Security

OpenAI engineer arrested for allegedly trying to eavesdrop on executive meetings

A recording device wrapped in toilet paper and plugged into the back of a television in an executive conference room at OpenAI’s San Francisco office has led to the arrest of one of the company’s engineers. Abdulrahman Alfozan, a 35-year-old Saudi national who had worked at OpenAI as an engineer since July 2025, was arrested on October 9 and charged with usi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification