
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 2,629 advisories
Page 33 of 110
Microsoft fixes exploited Mark of the Web bypass vulnerability (CVE-2026-96951) Critical CVE-2026-96951 Help Net Security
2026-10-14 Help Net Security

Microsoft fixes exploited Mark of the Web bypass vulnerability (CVE-2026-96951)

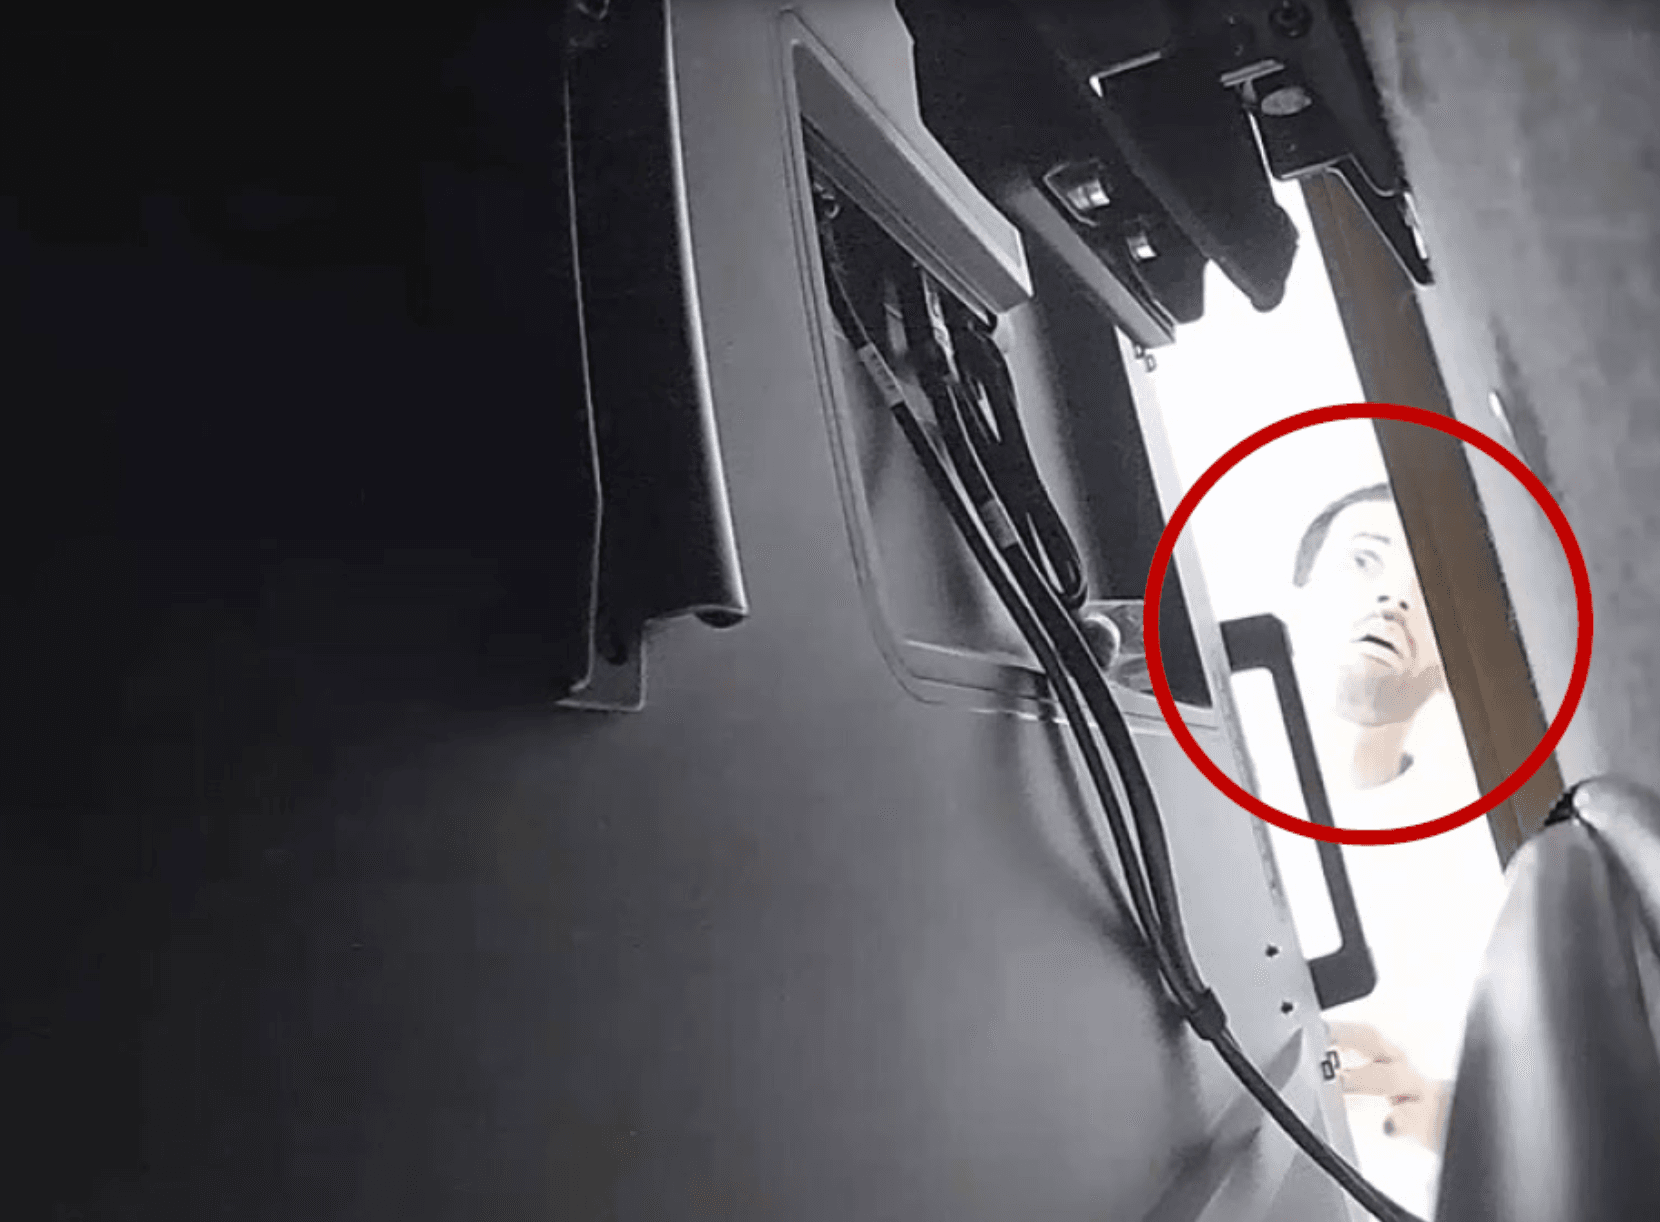
In another record-breaking Patch Tuesday, Microsoft has squashed over 1,400 security bugs, including a Mark of the Web bypass vulnerability (CVE-2026-96951) exploited by attackers in the wild. CVE-2026-96951 is a command injection vulnerability in Windows Shell that can be triggered by remote attackers via a file that is designed to exploit the vulnerability…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI-Found Linux Kernel Flaw Gives Local Users Root, and Can Break a Guest Out to the Host Important CVE-2026-74580 The Hacker News
2026-10-14 The Hacker News

AI-Found Linux Kernel Flaw Gives Local Users Root, and Can Break a Guest Out to the Host

A flaw in Linux's vhost subsystem lets a local user read and write kernel memory at will and become root across nearly a decade of kernel versions. In one virtualization setup, it lets an untrusted virtual machine write to the host's memory and hijack the program that runs the virtual machine. The bug is tracked as CVE-2026-74580 and named Vghost. Tencent Zh…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Orphaned VBA Projects Inside DWG Files, (Wed, Oct 14th) Moderate SANS Internet Storm Center
2026-10-14 SANS Internet Storm Center

Orphaned VBA Projects Inside DWG Files, (Wed, Oct 14th)

Years ago I wrote diary entries about VBA code stored inside AutoCAD drawing files (.dwg).

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Four-Byte Write and Timing Bug Let Researchers Run Code in Windows SmartScreen Enclave Moderate The Hacker News
2026-10-14 The Hacker News

Four-Byte Write and Timing Bug Let Researchers Run Code in Windows SmartScreen Enclave

Security researchers ran their own code inside a protected part of Windows that is meant to stay sealed off even when the rest of the computer is taken over. The protected area is a VBS enclave, an isolated slice of memory the operating system uses to guard secrets, and the one they broke into handles passwords for a Windows anti-phishing feature. The work w…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How a leaked builder of XWorm turned a remote access trojan into a surveillance kit Critical SecurityAffairs
2026-10-14 SecurityAffairs

How a leaked builder of XWorm turned a remote access trojan into a surveillance kit

Netskope tracks four XWorm versions in the wild, 46 plugins, and new tools for location, audio and live browser control, with detections up fourfold. Netskope Threat Labs has been following XWorm since September 2024, and its latest report shows the malware has changed a lot. Over the past year the team identified four distinct versions running at the same t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Patching and preventing issues: What are the lessons you can learn? Moderate Help Net Security
2026-10-14 Help Net Security

Patching and preventing issues: What are the lessons you can learn?

In this Help Net Security interview, Kunal Modasiya, Senior VP & GM at Qualys, talks about why patching is still hard to get right. He explains how business pressure, revenue-critical systems, and patches that break things keep fixes from going out. Modasiya argues that speed alone has limits and that teams should look at the whole remediation workflow. He d…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Meshery: Open-source cloud-native manager for Kubernetes Critical Help Net Security
2026-10-14 Help Net Security

Meshery: Open-source cloud-native manager for Kubernetes

Meshery is an open-source tool for designing, deploying and managing Kubernetes infrastructure, built by Layer5 and its community and hosted as a Cloud Native Computing Foundation project. Teams use it to lay out clusters and applications on a visual canvas, check the design, and push it to multiple clusters and clouds from one central console, without hand-…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Ransomware Gangs Embrace Physical Threats, Family Stalking? Critical Dark Reading
2026-10-14 Dark Reading

Ransomware Gangs Embrace Physical Threats, Family Stalking?

Organizations are reporting that employees face threats of stalking, physical violence, and abduction. But these alarming claims are hard to verify.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Patches Record 1,413 Flaws, Including Exploited Windows Shell Bug Important The Hacker News
2026-10-14 The Hacker News

Microsoft Patches Record 1,413 Flaws, Including Exploited Windows Shell Bug

Microsoft on Tuesday shattered its own Patch Tuesday record by shipping patches for a whopping 1,413 vulnerabilities, including one that it said has come under active exploitation. These include 1,102 flaws in Windows, 134 in Office, 61 in Developer Tools, 36 in SharePoint Server, and 22 in SQL Server. Of these, more than 670 relate to privilege escalation, …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Most companies count AI agents as insiders, and CISOs worry about their own liability Moderate Help Net Security
2026-10-14 Help Net Security

Most companies count AI agents as insiders, and CISOs worry about their own liability

Software that works on an employee’s behalf is now turning up in incident reports. At 95% of the companies in a Trellix survey of 600 CISOs, an AI agent or other autonomous system was linked to an insider incident in the past 12 months. The agent logs in, reaches sensitive systems, and acts for a person using that person’s permissions. Most respondents alrea…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google quadruples Chrome bug bounty base pay, offers up to $20,000 for sandbox escapes Moderate Help Net Security
2026-10-14 Help Net Security

Google quadruples Chrome bug bounty base pay, offers up to $20,000 for sandbox escapes

Google is updating its Chrome Vulnerability Rewards Program (Chrome VRP), increasing payments for memory corruption vulnerabilities and expanding rewards for other security flaws, fixes and research tools. “A primary goal of the Chrome VRP has always been to identify ways to improve our internal testing by understanding which vulnerabilities are the most sev…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI Employee Arrested for Allegedly Planting Hidden Recorder in Executive Conference Room Moderate The Hacker News
2026-10-14 The Hacker News

OpenAI Employee Arrested for Allegedly Planting Hidden Recorder in Executive Conference Room

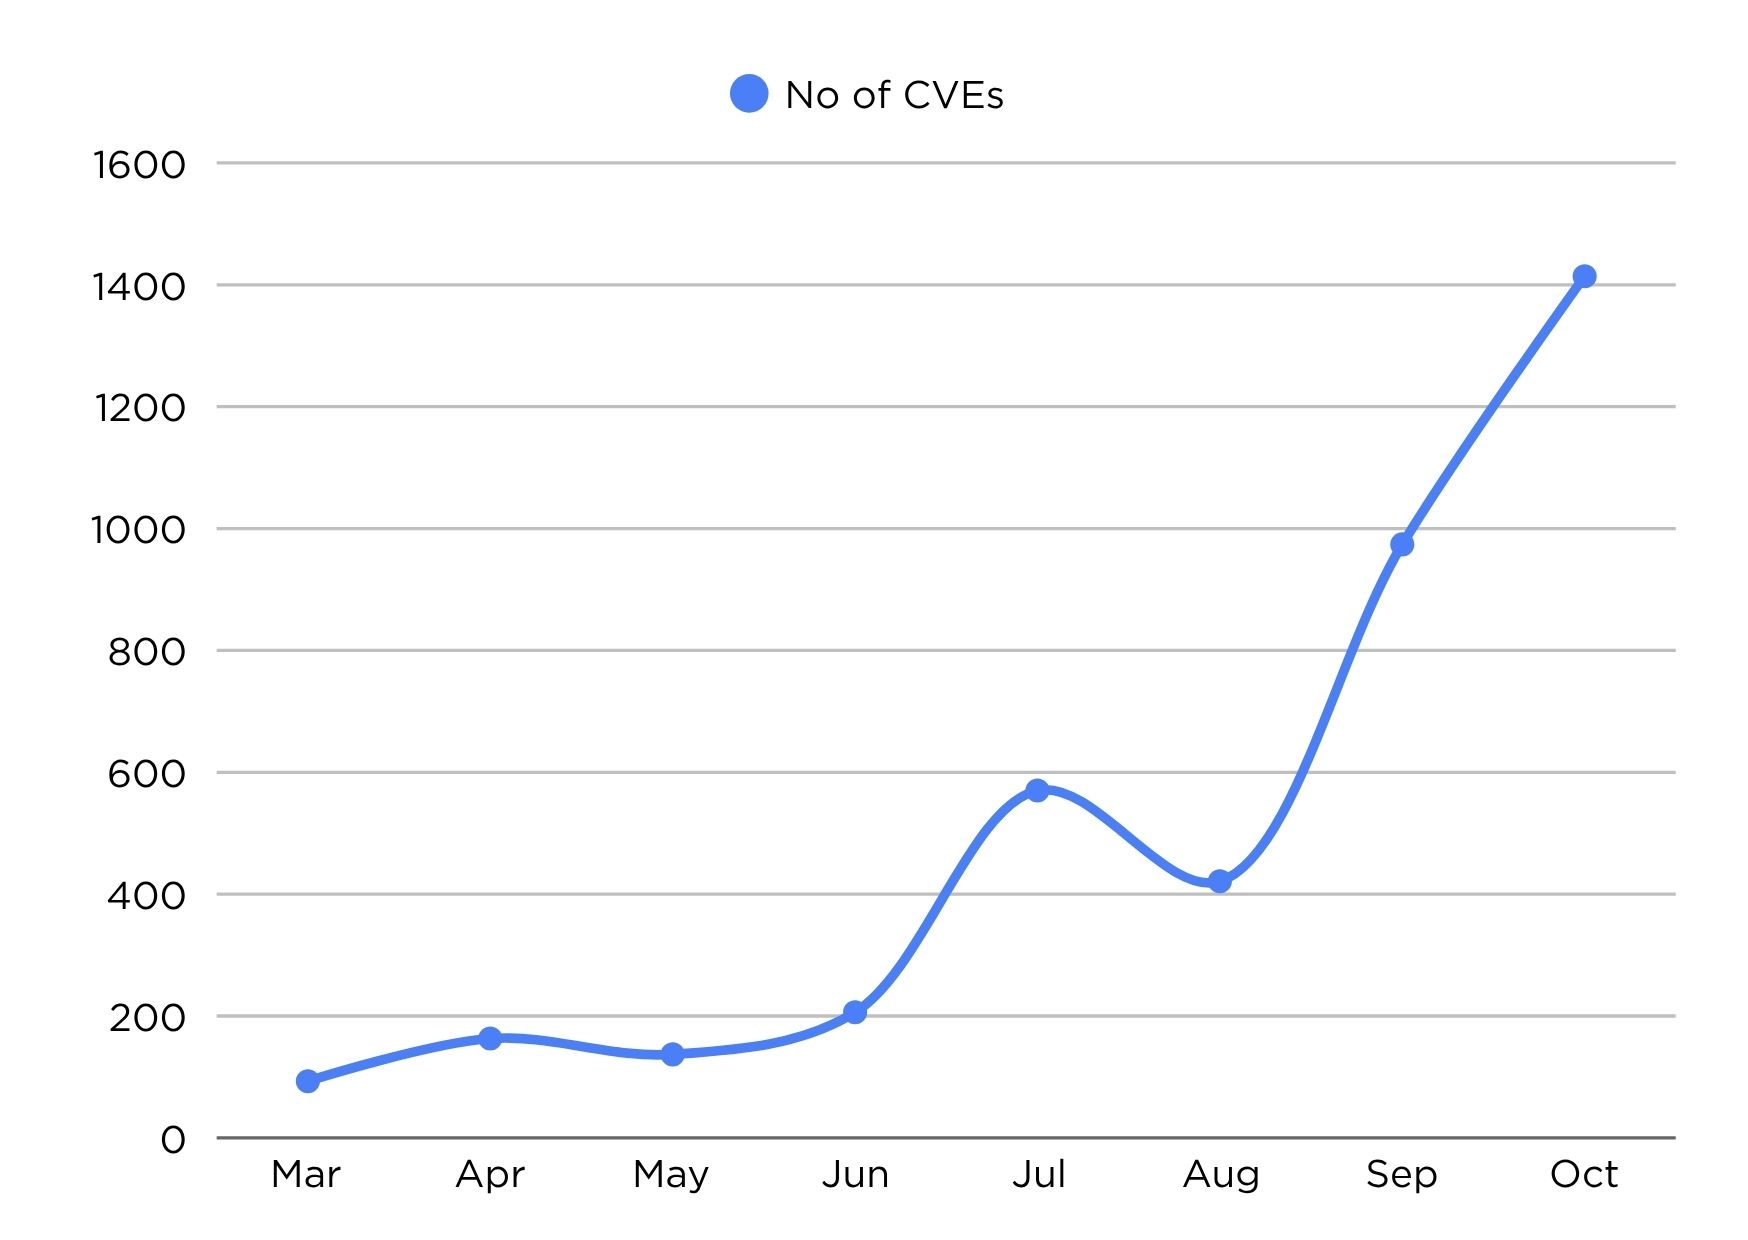
A Saudi national and employee of OpenAI has been arrested for allegedly planting a hidden recording device in an executive conference room at the company's San Francisco offices to covertly record sensitive conversations. Abdulrahman Alfozan, 35, has been charged with using or endeavoring to use an electronic, mechanical, or other device to intercept oral co…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Saudi national charged with planting spy device in OpenAI executive conference room Moderate The Record by Recorded Future
2026-10-13 The Record by Recorded Future

Saudi national charged with planting spy device in OpenAI executive conference room

Abdulrahman Alfozan, 35, a Saudi national working as an engineer for OpenAI, was charged Tuesday with secretly bugging an executive conference room at one of the company’s buildings in San Francisco.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
OpenAI engineer arrested for allegedly planting spy device in office Moderate BleepingComputer
2026-10-13 BleepingComputer

OpenAI engineer arrested for allegedly planting spy device in office

A Saudi OpenAI engineer has been arrested for allegedly planting a hidden recording device in an executive conference room at the company's San Francisco offices to secretly record sensitive conversations. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Noise Inside the Network: How an Unsophisticated Attack Exposed a Third-Party Risk Important Palo Alto Unit 42
2026-10-13 Palo Alto Unit 42

The Noise Inside the Network: How an Unsophisticated Attack Exposed a Third-Party Risk

Unit 42 dissects a cyberattack targeting a European bank's IT infrastructure, delivering concrete defense strategies to help organizations detect and counter comparable threats. The post The Noise Inside the Network: How an Unsophisticated Attack Exposed a Third-Party Risk appeared first on Unit 42 .

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Patch Tuesday - October 2026 Moderate CVE-2026-96951 Rapid7 Threat Research
2026-10-13 Rapid7 Threat Research

Patch Tuesday - October 2026

Microsoft is publishing 1,413 own-product vulnerabilities on October 2026 Patch Tuesday , including 1,102 vulnerabilities in Windows. Anyone who enjoyed last month’s record-setting Patch Tuesday will love the October 2026 edition, because it’s much bigger still. As Rapid7 has noted over the course of 2026, there is every reason to suppose that vulnerability …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Ghostscript flaw lets hackers hijack servers via PDF uploads Critical CVE-2026-39919 BleepingComputer
2026-10-13 BleepingComputer

Ghostscript flaw lets hackers hijack servers via PDF uploads

A critical heap buffer overflow vulnerability (CVE-2026-39919) in the Ghostscript interpreter and rendering engine could allow remote code execution through specially crafted PDF files. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Patch Tuesday, October 2026 Security Update Review Critical CVE-2026-96951 Qualys Security Blog
2026-10-13 Qualys Security Blog

Microsoft Patch Tuesday, October 2026 Security Update Review

Microsoft has released its October 2026 Patch Tuesday security updates, addressing vulnerabilities across its products and services. As organizations continue to navigate an evolving threat landscape, applying security patches promptly remains critical to reducing exposure and strengthening security posture. This month’s updates highlight the importance of i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
North Korea Phishes Ukrainians for War Intel Moderate Dark Reading
2026-10-13 Dark Reading

North Korea Phishes Ukrainians for War Intel

The Democratic People's Republic of Korea (DPRK) is trying to get insight into its own war effort in Ukraine, through simple reply-baiting phishing attacks.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Anthropic warns self-replicating AI could spread to your smart devices Moderate BleepingComputer
2026-10-13 BleepingComputer

Anthropic warns self-replicating AI could spread to your smart devices

Anthropic is warning that small AI models could soon be able to self-replicate across consumer IoT devices, from Android TV boxes to smart ovens, creating distributed botnets capable of running AI workloads without relying on data centers. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Patch Tuesday for October 2026 — Snort rules and prominent vulnerabilities Critical CVE-2026-96951 Cisco Talos Intelligence
2026-10-13 Cisco Talos Intelligence

Microsoft Patch Tuesday for October 2026 — Snort rules and prominent vulnerabilities

Microsoft has released its monthly security update for October 2026, which includes 1415 vulnerabilities affecting a range of products, including 85 that Microsoft marked as "critical." Microsoft notes that 1 of the vulnerabilities disclosed this month have been exploited in the wild CVE-2026-96951 is a security feature bypass vulnerability that affects Wind…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification