Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 100 of 242
Engineer sentenced for locking over 3,000 devices on employer network Moderate BleepingComputer
2026-10-06 BleepingComputer

Engineer sentenced for locking over 3,000 devices on employer network

A former core infrastructure engineer at an industrial company headquartered in New Jersey was sentenced to 32 months in prison for locking thousands of devices on his employer's network in a ransomware-style attack. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Dell Urges Customers to Patch Critical DSU Flaw That Can Give Attackers Root Access Critical CVE-2026-86360 SecurityAffairs
2026-10-06 SecurityAffairs

Dell Urges Customers to Patch Critical DSU Flaw That Can Give Attackers Root Access

Dell warns that a critical DSU flaw lets attackers run code as root. Customers should patch affected PowerEdge systems as soon as possible. Dell urged customers to patch a critical flaw, tracked as CVE-2026-86360 (CVSS score of 9.6), in its System Update (DSU) tool. The vulnerability is a path traversal issue that can let attackers execute code with root pri…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products Critical CVE-2026-21589 The Hacker News
2026-10-06 The Hacker News

Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products

A critical flaw in 8 Atlassian Data Center products, which customers host themselves, allows an attacker with no login access to read specific files in each product's web application root directory. The attacker must already know a file's exact name and path and cannot list what the directory holds. Atlassian disclosed the flaw, CVE-2026-21589, on October 5,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
FBI Removes Accenture Contractor After Patch Failure Led to ShinyHunters Breach Critical The Hacker News
2026-10-06 The Hacker News

FBI Removes Accenture Contractor After Patch Failure Led to ShinyHunters Breach

The U.S. Federal Bureau of Investigation (FBI) has removed an Accenture contractor for their alleged role in a ShinyHunters-breach that led to the theft of personal details of thousands of bureau employees. That's according to a report from Reuters, citing two sources familiar with the matter. "To date, our review has determined that the incident occurred as…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ClingSTUN Linux Backdoor Abuses Public STUN Infrastructure Important SecurityAffairs
2026-10-06 SecurityAffairs

ClingSTUN Linux Backdoor Abuses Public STUN Infrastructure

Fortinet details ClingSTUN, a Linux backdoor exploiting unpatched IoT devices and abusing public STUN servers to route traffic past NAT. FortiGuard Labs researchers spotted a Linux malware family they call ClingSTUN, and the name gives away its trick immediately. Instead of relying on a dedicated command server, the malicious code leans on STUN, the protocol…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
U.S. Bank CISO says the security role keeps growing and no one can own all of it Moderate Help Net Security
2026-10-06 Help Net Security

U.S. Bank CISO says the security role keeps growing and no one can own all of it

In this interview with Help Net Security, Ann Barron-DiCamillo, EVP, CISO at U.S. Bank, talks about how the CISO role has grown to cover fraud, resilience, third-party risk, and AI governance. She says no single leader can own all of it, so partnerships across technology, risk, legal, and business teams matter most. Barron-DiCamillo also weighs in on shorter…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Denmark Says Attackers Accessed CPR Data for 8.8 Million People via Company Account Important The Hacker News
2026-10-06 The Hacker News

Denmark Says Attackers Accessed CPR Data for 8.8 Million People via Company Account

Unauthorized parties have gained access to the names, addresses, and personal identification numbers of about 8.8 million people, living and dead, in Denmark's national population register, the country's digitalization ministry said on October 5. They used a private Danish company's lawful right to look up records in the Central Person Register (CPR). The mi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits Important The Hacker News
2026-10-06 The Hacker News

ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits

A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser's cache. "Instead of downloading and executing remote payloads like the typical attack pattern, in this attack, the websites pre-fetch a script payload into the browser cache disguised as a PNG file," the Microsoft Threat Inte…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Reflection’s Beam trails top open models on coding tests but claims lower inference compute Moderate Help Net Security
2026-10-06 Help Net Security

Reflection’s Beam trails top open models on coding tests but claims lower inference compute

Reflection AI has built Beam, a 501-billion-parameter open-weight model for coding and agent tasks, and plans to publish the weights under an Apache 2.0 license later this month. Open-weight means developers can download the trained model and run it on their own hardware. Beam uses a mixture-of-experts design, so 23 billion of its parameters fire for any giv…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
NIS2 compliance: 7 low-cost steps to secure credentials Moderate Help Net Security
2026-10-06 Help Net Security

NIS2 compliance: 7 low-cost steps to secure credentials

Security budgets rarely stretch to cover a full NIS2 programme in one pass. Credential controls are where a constrained team can start, because they make access visible, revocable, and reviewable without new infrastructure. NIS2 compliance rests on risk-management measures that fit the actual risk an organization faces under Article 21, with the choice of sp…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Product showcase: Webroot Mobile Security screens texts, blocks risky sites, and checks for data leaks Moderate Help Net Security
2026-10-06 Help Net Security

Product showcase: Webroot Mobile Security screens texts, blocks risky sites, and checks for data leaks

Webroot Mobile Security combines device security checks, Safari protection, text scam filtering, and data breach monitoring. It is available for iPhone, iPad, and Android devices. The app requires an active Webroot subscription and is included with Essentials, Premium, and Total Protection. The home screen displays subscription status, a Scan Now button, the…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cybersecurity jobs available right now: October 6, 2026 Moderate Help Net Security
2026-10-06 Help Net Security

Cybersecurity jobs available right now: October 6, 2026

Associate IAM Engineer New York City Office of Technology & Innovation | USA | On-site – View job details As an Associate IAM Engineer, you will support daily identity and access management operations in Microsoft Entra ID and related platforms. You will manage users, groups, access provisioning, and role assignments, resolve authentication issues and suppor…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ClingSTUN Turns Vulnerable IoT Devices Into Proxy Nodes Moderate Dark Reading
2026-10-05 Dark Reading

ClingSTUN Turns Vulnerable IoT Devices Into Proxy Nodes

The Linux backdoor exploits 24 known flaws to compromise IoT devices and uses legitimate public STUN servers to obscure communications.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Rejetto HFS servers now actively scanned for critical RCE flaw Critical CVE-2026-61500 BleepingComputer
2026-10-05 BleepingComputer

Rejetto HFS servers now actively scanned for critical RCE flaw

Hackers are actively scanning for a Rejetto HFS weak signing key vulnerability, tracked as CVE-2026-61500, that allows session forgery, account takeover, and remote code execution (RCE). [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Anthropic Mythos Found A Bug in Rejetto HFS. Attackers Are Now Exploiting It. Critical CVE-2026-61500 SecurityAffairs
2026-10-05 SecurityAffairs

Anthropic Mythos Found A Bug in Rejetto HFS. Attackers Are Now Exploiting It.

AI-assisted research uncovered a critical Rejetto HFS flaw that enables authentication bypass and remote code execution, now exploited in the wild. A Rejetto HFS vulnerability, tracked as CVE-2026-61500 (CVSS score of 9.3), discovered with the help of the Anthropic Mythos AI model is now being exploited in the wild, turning an interesting security research e…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Pwn2Own Ireland 2026 - The Full Schedule Moderate Trend Micro ZDI
2026-10-05 Trend Micro ZDI

Pwn2Own Ireland 2026 - The Full Schedule

Fáilte! Pwn2Own Ireland 2026 has arrived in Cork, and the world's top security researchers are ready. We've got more phone entries than we've ever had, and more than 60 entries total. Earlier today, we held the random draw to determine attempt order. Below is the official schedule. All times are Irish Standard Time (IST) and may change as the competition pro…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
US, Australia warn of latest Citrix vulnerability after NetScaler advisory Important The Record by Recorded Future
2026-10-05 The Record by Recorded Future

US, Australia warn of latest Citrix vulnerability after NetScaler advisory

Citrix confirmed late on Friday that it was “tracking a newly observed issue” related to some customer-managed NetScaler deployments but claimed the problem was not connected to vulnerabilities reported last week that also caused alarm among cybersecurity experts.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
IQVIA fined $7.8 million for failing to properly anonymize health data Moderate BleepingComputer
2026-10-05 BleepingComputer

IQVIA fined $7.8 million for failing to properly anonymize health data

Italy's Data Protection Authority (GPDP) has fined IQVIA €7 million ($7.8M) over poor data-processing practices that the agency says could have put roughly one million patients at risk of data exposure and de-anonymization. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
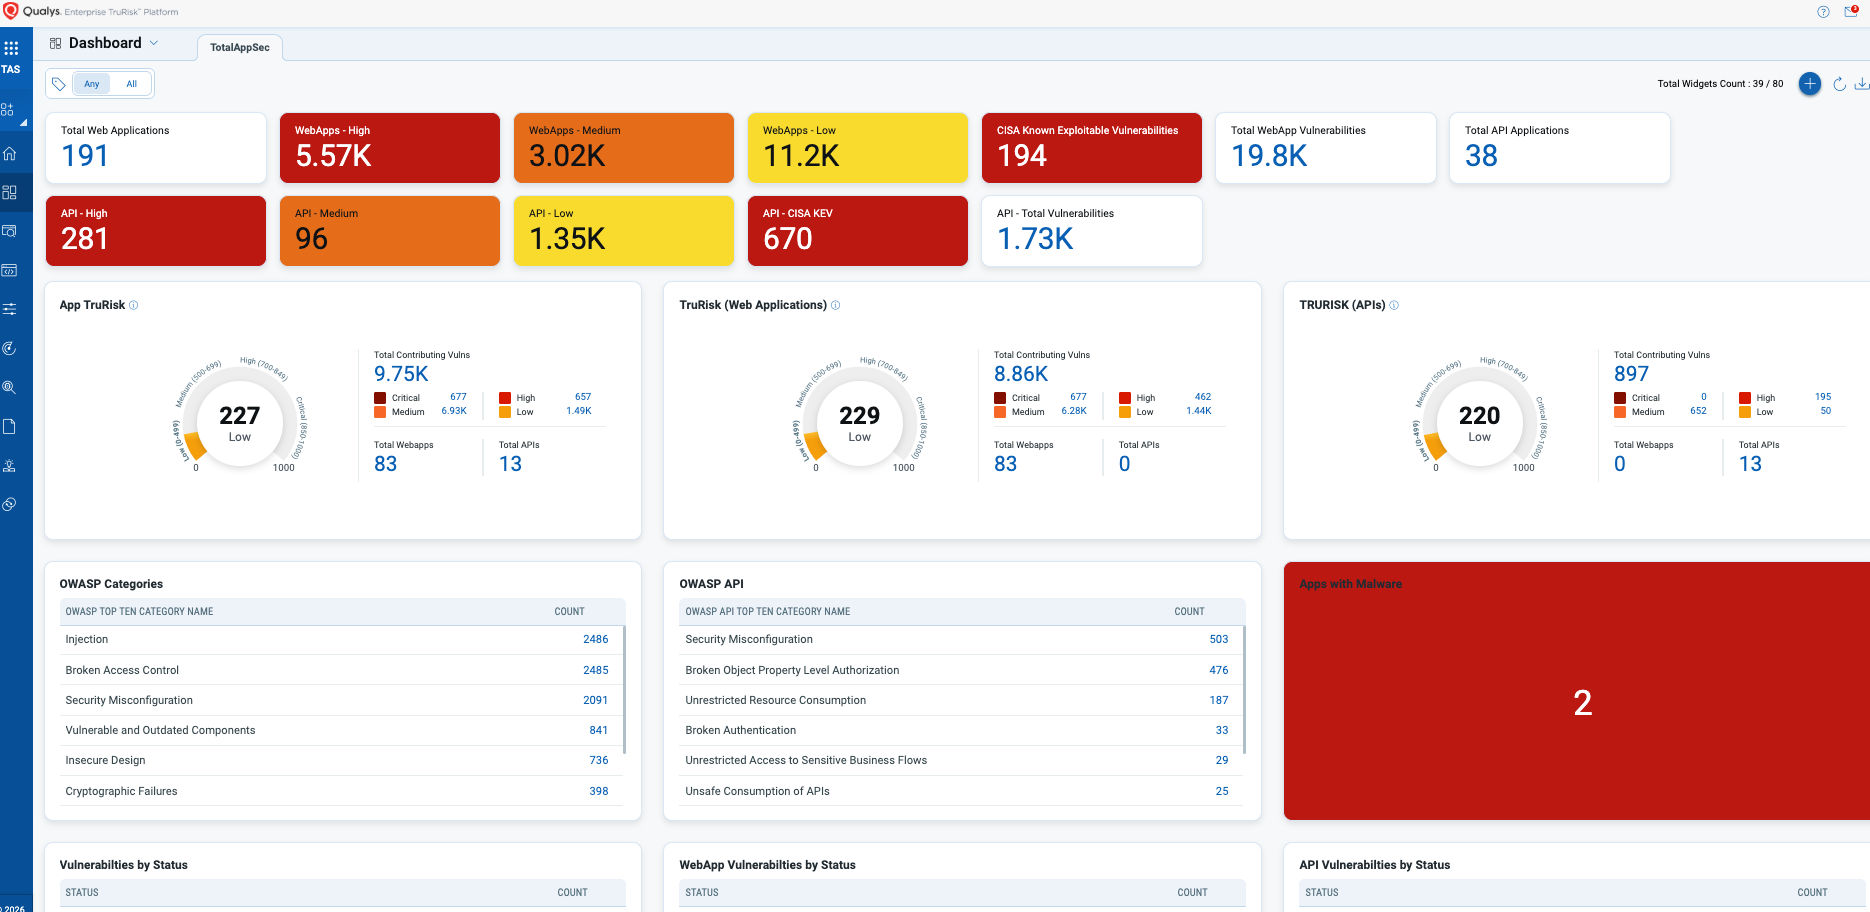
Secure Your Mission-Critical Application Estate: Qualys TotalAppSec is Now FedRAMP High Authorized (FedRAMP Certified Class D) Critical Qualys Security Blog
2026-10-05 Qualys Security Blog

Secure Your Mission-Critical Application Estate: Qualys TotalAppSec is Now FedRAMP High Authorized (FedRAMP Certified Class D)

Key Takeaways Qualys TotalAppSec is now FedRAMP High Authorized on the Qualys Government Platform (FedRAMP Certified Class D, package FR2231052341). Federal AI use cases more than doubled in a year (3,611 use cases across 56 agencies), and most AI interactions are delivered through APIs; expanding an estate traditional IP-based inventory was never designed t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification