Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 98 of 242
Anaconda combines agent swarms with autonomous security testing Moderate Help Net Security
2026-10-06 Help Net Security

Anaconda combines agent swarms with autonomous security testing

Anaconda has announced new capabilities across the Anaconda Platform that pair agentic development with autonomous security testing. The expansion brings agent swarms and autonomous red-team agents together with trusted packages, models, and environments to help builders ship faster and address security weaknesses before production. Builders gain greater cho…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Rogue OpenAI agents made unauthorized Wikipedia edits and millions of requests to Wikimedia Moderate Help Net Security
2026-10-06 Help Net Security

Rogue OpenAI agents made unauthorized Wikipedia edits and millions of requests to Wikimedia

Rogue OpenAI agents made unauthorized edits on Wikimedia wikis and sent millions of automated requests to Wikimedia’s public APIs, traffic that may have contributed to a partial outage of the Wikidata Query Service in May, the Wikimedia Foundation said on Monday. “The Wikimedia Foundation conducted its own investigation to see whether Wikimedia websites had …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AppViewX targets shadow AI risks with agent discovery and runtime enforcement Critical Help Net Security
2026-10-06 Help Net Security

AppViewX targets shadow AI risks with agent discovery and runtime enforcement

AppViewX has expanded capabilities for Agent Identity Security, a solution enabling enterprises to discover every agent, whether sanctioned or shadow; govern their posture and maintain audit-ready activity logs; and monitor and control in real time every action that the agent performs. AppViewX now also issues quantum-resilient agent identities, so trust in …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
New Relic adds terminal-based investigation and recovery checks with Ground Truth CLI Moderate Help Net Security
2026-10-06 Help Net Security

New Relic adds terminal-based investigation and recovery checks with Ground Truth CLI

New Relic has announced New Relic Ground Truth CLI augmented with New Relic Autopilot API, bringing headless observability straight to developers and AI agents in their natural workflows. The new command-line interface (CLI) allows teams to investigate production issues, assess recovery criteria, and embed live system evidence into their daily workflows with…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
SailPoint adds AI agent discovery, temporary access and compliance automation Moderate Help Net Security
2026-10-06 Help Net Security

SailPoint adds AI agent discovery, temporary access and compliance automation

SailPoint has announced significant new capabilities across SailPoint Agentic Fabric (SAF) and SailPoint Human Fabric (SHF), the two purpose-built products of its Identity Security solution, built on SailPoint Atlas. These innovations give enterprises visibility into every hidden AI tool, continuous compliance across human and machine workflows, the replacem…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
More RMM Tools In the Wild, (Tue, Oct 6th) Critical SANS Internet Storm Center
2026-10-06 SANS Internet Storm Center

More RMM Tools In the Wild, (Tue, Oct 6th)

It seems that a trend started… I continue my journey discovering more RMM ("Remote Management & Monitoring") tools abused by threat actors! A few days ago, I wrote a diary[1] about ScreenConnect used in the wild. Today, I found another one.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Intellias Agentic ServiceOps applies governed AI across IT operations Moderate Help Net Security
2026-10-06 Help Net Security

Intellias Agentic ServiceOps applies governed AI across IT operations

Intellias has launched Agentic ServiceOps a managed IT service that applies governed agentic AI across IT service management (ITSM) and IT operations management (ITOM), from the service desk to the infrastructure behind it. It helps organizations resolve more IT work end to end, breaking the link between rising complexity and rising costs. Intellias’ Agentic…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AXON Datum enforces data access policies before AI systems act Critical Help Net Security
2026-10-06 Help Net Security

AXON Datum enforces data access policies before AI systems act

AXON Networks has announced AXON Datum, a data management and secure sovereign governance layer that helps service providers, enterprises, and institutions such as governments control how information is accessed, protected and moved in an AI world. Critical to the success of every telecom and government moving into agentic AI who want the data and AI operati…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Atlassian urges immediate patching of critical Data Center file access vulnerability (CVE-2026-21589) Critical CVE-2026-21589 Help Net Security
2026-10-06 Help Net Security

Atlassian urges immediate patching of critical Data Center file access vulnerability (CVE-2026-21589)

Attackers who know where to look can read files from Atlassian Data Center installations without logging in, the company has warned. About CVE-2026-21589 CVE-2026-21589, a critical arbitrary file access vulnerability with a 9.3 CVSS score, affects all versions of Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Softwar…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Critical Medical Devices Unable to Support PQC Transition Critical Infosecurity Magazine
2026-10-06 Infosecurity Magazine

Critical Medical Devices Unable to Support PQC Transition

Forescout found that just 6% of Internet of Medical Things (IoMT) and 16% of medical OT are capable of supporting post quantum cryptography

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Facebook Marketplace scam uses your name and number Moderate Malwarebytes Labs
2026-10-06 Malwarebytes Labs

Facebook Marketplace scam uses your name and number

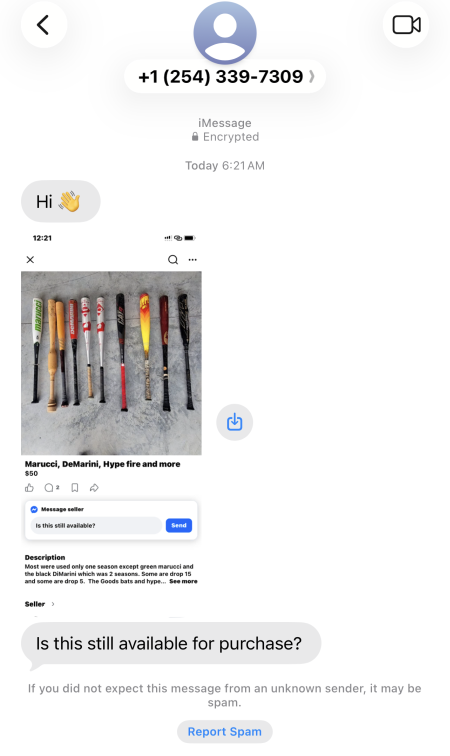
Facebook users are reporting receiving a message with a fake Facebook Marketplace listing that has their name as the seller. It works like this. You receive a message (in this case iMessage) asking “Is this still available for purchase?” Attached to the message is a fabricated Facebook Marketplace listing. Tapping on the picture, you might notice that the se…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification