
Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 5,807 advisories
Page 97 of 242
Automation, AI agents or people? Sorting out who handles each security finding Moderate Help Net Security
2026-10-07 Help Net Security

Automation, AI agents or people? Sorting out who handles each security finding

Just over half of the 200 senior security and technology leaders polled for ArmorCode say their organizations will struggle to simplify their software security programs if they keep working the way they do today. The respondents are senior people, most of them at companies with 10,000 or more employees, and their worries center on what happens after a scanne…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Check your X.Org server version because a dozen vulnerabilities have been patched Critical CVE-2026-93524 Help Net Security
2026-10-07 Help Net Security

Check your X.Org server version because a dozen vulnerabilities have been patched

X.Org fixed 12 security flaws in the X server and Xwayland, with the repairs shipping in xorg-server 21.1.25 and xwayland-24.1.14. Nine of the flaws can lead to arbitrary code execution. The other three can crash the server or disclose information. Ten of the 12 entries say an authenticated X client can trigger the flaw, meaning a program the server already …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Ninja Forms plugin flaw exploited to hack WordPress sites Critical BleepingComputer
2026-10-06 BleepingComputer

Ninja Forms plugin flaw exploited to hack WordPress sites

Hackers are exploiting stored cross-site scripting (XSS) vulnerabilities in two unrelated WordPress plugins, Ninja Forms and WPC Product Bundles for WooCommerce, to install backdoors and create rogue admin accounts. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

ClickFix Attacks Evolve to Better Hide Malicious Payloads Important Dark Reading
2026-10-06 Dark Reading

ClickFix Attacks Evolve to Better Hide Malicious Payloads

Threat actors are now hiding payloads by using DNS TXT records and browser cache pre-fetching, making it tougher to spot early attack stages.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Critical Healthcare Systems Aren't Quantum-Ready Critical Dark Reading
2026-10-06 Dark Reading

Critical Healthcare Systems Aren't Quantum-Ready

A study of 2.5 million devices across 50 healthcare organizations suggests the sector has a long way to go in getting ready for the post-quantum cryptography era.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Hackers exploit 32 zero-days on first day of Pwn2Own Ireland Critical BleepingComputer
2026-10-06 BleepingComputer

Hackers exploit 32 zero-days on first day of Pwn2Own Ireland

On the first day of the Pwn2Own Ireland 2026 competition, security researchers hacked the Samsung Galaxy S26 twice and earned $388,500 after exploiting 32 zero-days. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Fake ChatGPT, Gemini, and Claude Ad Portals Capture Credentials and MFA Codes Moderate The Hacker News
2026-10-07 The Hacker News

Fake ChatGPT, Gemini, and Claude Ad Portals Capture Credentials and MFA Codes

Cybersecurity researchers have disclosed details of a "human-operated phishing platform" that impersonates advertising products for artificial intelligence (AI) chatbots like Google Gemini, Anthropic Claude, OpenAI ChatGPT, Perplexity, Meta Muse, and Manus. The products, which claim to offer campaign optimization, spend audits, and business-account connectio…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Linux Backdoors Impersonate Email Security Tools to Evade Detection in Korea and Taiwan Important The Hacker News
2026-10-06 The Hacker News

Linux Backdoors Impersonate Email Security Tools to Evade Detection in Korea and Taiwan

Linux backdoors targeting telecom and network appliances in South Korea and Taiwan have been disguising their traffic as email services and seemingly legitimate processes to blend in and evade detection. Threat actors are known to name their malicious software after a legitimate operating system component or a process as a defense evasion measure. By borrowi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Google's PageBreak AI Agent Finds 500 Flaws in Its Web Apps Important Dark Reading
2026-10-06 Dark Reading

Google's PageBreak AI Agent Finds 500 Flaws in Its Web Apps

The situation illustrates a trend toward using AI and deterministic validation to identify flaws and exploitability, and provide a risk assessment.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Atlassian warns of critical file-access flaw in Jira, Confluence Critical CVE-2026-21589 BleepingComputer
2026-10-06 BleepingComputer

Atlassian warns of critical file-access flaw in Jira, Confluence

Atlassian is warning customers of a critical vulnerability, tracked as CVE-2026-21589, that can be exploited for arbitrary file-access in multiple self-hosted Data Center products, including Confluence, Jira, and Bitbucket. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ASOS confirms data breach after “HACKED” in-app notifications Critical BleepingComputer
2026-10-06 BleepingComputer

ASOS confirms data breach after “HACKED” in-app notifications

UK fashion retailer ASOS confirmed a data breach Tuesday after hackers sent unauthorized push notifications through its mobile app while claiming to have stolen customer data from the company's Snowflake environment. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Alleged ATM malware creator appears in Nebraska court after arrest Important The Record by Recorded Future
2026-10-06 The Record by Recorded Future

Alleged ATM malware creator appears in Nebraska court after arrest

Aguirre was added to the FBI’s “Top 10 Most Wanted Fugitives” list in March, becoming the first cybercriminal added to the list.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
South Korean officials believe AI agents were used to hack several banks Moderate The Record by Recorded Future
2026-10-06 The Record by Recorded Future

South Korean officials believe AI agents were used to hack several banks

The personal data of at least 68,000 people was reportedly exposed in breaches of at least seven financial institutions, with officials saying they believe a Chinese cybersecurity tool was used to hack the banks’ systems.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Fake ChatGPT, Gemini Sites steal advertising accounts, MFA codes Moderate BleepingComputer
2026-10-06 BleepingComputer

Fake ChatGPT, Gemini Sites steal advertising accounts, MFA codes

A new campaign targeting ad account managers uses fake ChatGPT, Gemini, Claude, and Perplexity sites that steal login credentials and multi-factor authentication (MFA) codes through browser-in-browser attacks. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ClickFix Attack Hides VBScript Payload in Browser Cache Important Infosecurity Magazine
2026-10-06 Infosecurity Magazine

ClickFix Attack Hides VBScript Payload in Browser Cache

ClickFix sites stage a VBScript payload in the browser cache to bypass the Run dialog's length limit

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
ASOS “hackers” send push notifications to customers Important Malwarebytes Labs
2026-10-06 Malwarebytes Labs

ASOS “hackers” send push notifications to customers

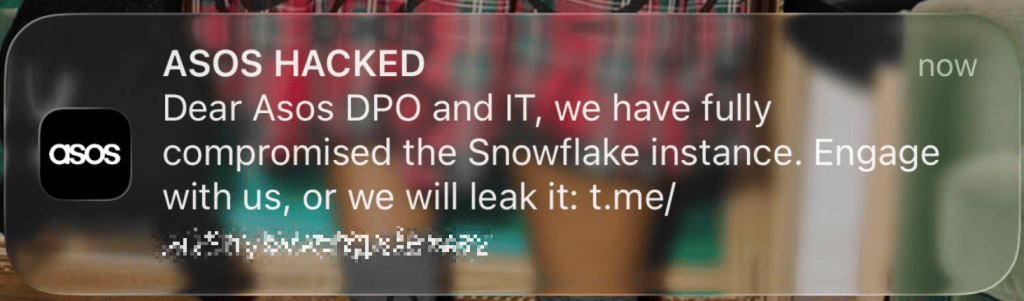
Thousands of global fashion retailer ASOS customers have received a push notification through the ASOS app this morning alleging that the company has been hacked. The notification, addressed to ASOS’s data protection officer and IT, says: “ASOS HACKED Dear Asos DPO and IT, we have fully compromised ​the Snowflake instance. Engage with us, or we will leak it”…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Securing Agent-to-Agent Communication: The Next Identity Frontier Moderate Rapid7 Threat Research
2026-10-06 Rapid7 Threat Research

Securing Agent-to-Agent Communication: The Next Identity Frontier

As organizations deploy autonomous AI agents, security teams face a significant shift as non-human non-human entities making decisions, invoking tools, and delegating tasks to other agents without human intervention. Security architectures built around human users, static APIs, and distinct endpoints break down when AI agents dynamically collaborate across a…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-96940: Microsoft Fixes Exchange Server Flaw For Which Exploitation Is More Likely Important CVE-2026-96940 SecurityAffairs
2026-10-06 SecurityAffairs

CVE-2026-96940: Microsoft Fixes Exchange Server Flaw For Which Exploitation Is More Likely

Microsoft released emergency updates for Exchange Server to fix CVE-2026-96940, a high-severity flaw that can let attackers gain higher privileges. Microsoft has released out-of-band security updates for Exchange Server to fix a high-severity vulnerability tracked as CVE-2026-96940 (CVSS score of 8.8). The flaw is caused by weak authorization and can allow a…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How to secure RMM software: 8 controls MSPs should test Moderate BleepingComputer
2026-10-06 BleepingComputer

How to secure RMM software: 8 controls MSPs should test

RMM platforms give MSPs privileged access across customer environments, making their security controls critical to limiting risk. Acronis outlines eight controls MSPs should test when evaluating RMM software, from patching and privileged access to recovery and tenant isolation. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

Nikkei Discloses Two Employee Cloud Account Compromises Moderate Infosecurity Magazine
2026-10-06 Infosecurity Magazine

Nikkei Discloses Two Employee Cloud Account Compromises

Nikkei says two employee cloud accounts were accessed, with one used to send 9,000 phishing emails

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification