Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 608 advisories
Page 3 of 26
Big Fish: OpenBSD Root Exploit Chains a 37-Year-Old BSD Bug With a Kernel Flaw Important SecurityAffairs
2026-10-19 SecurityAffairs

Big Fish: OpenBSD Root Exploit Chains a 37-Year-Old BSD Bug With a Kernel Flaw

OpenBSD flaws, including a 37-year-old BSD bug, enable local attackers to bypass security protections and gain root access. Patches are available. Cybersecurity firm Calif published a full exploit and write-up this week for a local privilege escalation on OpenBSD 7.9 that chains two separate kernel flaws, one of them a 37-year-old integer overflow inherited …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Japan’s SiteGuard WAF flaw CVE-2026-106931 is already being exploited Critical CVE-2026-106931 SecurityAffairs
2026-10-19 SecurityAffairs

Japan’s SiteGuard WAF flaw CVE-2026-106931 is already being exploited

Attackers are exploiting vulnerability CVE-2026-106931 in SiteGuard Server Edition to run commands as root or SYSTEM. EG Secure Solutions published an urgent alert warning of CVE-2026-106931, an OS command injection bug in SiteGuard Server Edition. Threat actors are already exploiting it in the wild. A successful exploit lets them run commands with root or S…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Security Affairs newsletter Round 600 by Pierluigi Paganini – INTERNATIONAL EDITION Moderate CVE-2026-97229 SecurityAffairs
2026-10-18 SecurityAffairs

Security Affairs newsletter Round 600 by Pierluigi Paganini – INTERNATIONAL EDITION

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. North Korean IT Workers Used Stolen US Identities to Earn $3 Million U.S. CISA adds Fortinet Multiple Products an…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Targeted ads installed Candiru spyware in zero-click attacks Critical BleepingComputer
2026-10-16 BleepingComputer

Targeted ads installed Candiru spyware in zero-click attacks

Candiru spyware was delivered to devices at Al Jazeera Media Network via targeted online advertisements in a zero-click attack that required only rendering the malicious ads on the victim's device. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA Adds Two Known Exploited Vulnerabilities to Catalog Critical CISA Advisory
2026-10-16 CISA Advisory

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2025-61624 Fortinet Multiple Products Path Traversal Vulnerability CVE-2026-102764 BeyondTrust Remote Support Authentication Bypass by Spoofing Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management requirements for Federal Civilian Executive Branch (FCEB) agencies. BOD 26-04 reinforces the importance of the KEV Catalog and requires federal agencies to prioritize rapid remediation of high-risk vulnerabilities, specifically those identified by Common Vulnerabilities and Exposures (CVEs) listed in CISA’s KEV Catalog on publicly exposed assets that grant total control of the asset post-exploitation, while deferring action for lower-risk vulnerabilities. BOD 26-04 further establishes basic expectations for when agencies must check whether threat actors compromised the system before the patch was applied. While BOD 26-04 applies only to FCEB agencies, CISA encourages all organizations to adopt risk-based vulnerability management and prioritize remediation of KEV Catalog vulnerabilities . CISA will continue to add vulnerabilities to the catalog that meet the specified criteria . Aware of an exploited vulnerability not currently listed in the KEV Catalog? Submit it for potential addition through CISA’s KEV Nomination Form . Potential KEV additions must have a CVE ID, evidence of exploitation, and clear mitigation guidance.

Fix: Review CISA guidance and apply vendor security updates immediately.

China-Linked Hackers Exploited BeyondTrust Zero-Day to Take Over Remote Support Servers Critical CVE-2026-102764 The Hacker News
2026-10-16 The Hacker News

China-Linked Hackers Exploited BeyondTrust Zero-Day to Take Over Remote Support Servers

The China-nexus cyber espionage group tracked as Armory Castle (previously UNC5221 or Warp Panda) exploited a newly disclosed security flaw in BeyondTrust Remote Support (formerly Bomgar) as a zero-day in late August 2026. The vulnerability, tracked as CVE-2026-102764 (CVSS score: 9.3), is a case of improper origin validation in an internal messaging compone…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
BeyondTrust patches zero-day exploited in attacks since August Critical BleepingComputer
2026-10-16 BleepingComputer

BeyondTrust patches zero-day exploited in attacks since August

BeyondTrust warned customers on Thursday to patch a critical flaw in its Remote Support (RS) that has been exploited in zero-day attacks since late August. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
U.S. CISA adds Palo Alto Networks PAN-OS, Ahsay AhsayCBS, and Cisco Secure Email Gateway flaws to its Known Exploited Vulnerabilities catalog Important CVE-2026-0322 SecurityAffairs
2026-10-15 SecurityAffairs

U.S. CISA adds Palo Alto Networks PAN-OS, Ahsay AhsayCBS, and Cisco Secure Email Gateway flaws to its Known Exploited Vulnerabilities catalog

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Palo Alto Networks PAN-OS, Ahsay AhsayCBS, and Cisco Secure Email Gateway flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog : CVE-2026-0…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Zero-click spyware infecting devices through online ads, researchers say Critical The Record by Recorded Future
2026-10-15 The Record by Recorded Future

Zero-click spyware infecting devices through online ads, researchers say

Powerful zero-click spyware is infected devices worldwide through targeted ads, new research shows — an alarming development in the spread of surveillance technology.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Q3 Vulnerability Pulse: Discovery ≠ Exploitation Critical CVE-2014-125110 Cisco Talos Intelligence
2026-10-15 Cisco Talos Intelligence

The Q3 Vulnerability Pulse: Discovery ≠ Exploitation

Welcome to this week’s edition of the Threat Source newsletter. I've been following a lot of (sometimes heated) threads and discussions lately about the current vulnerability landscape. I learned new words/phrases such as Summer of Hell (although I'm writing this with 1°C/34°F outside), Vulnpocalypse, Bugmageddon, Bugpocalypse, Breachpocalypse... Let's look …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Citizen Lab Traces Zero-Click Candiru Spyware Infections at Al Jazeera to Targeted Online Ads Critical The Hacker News
2026-10-15 The Hacker News

Citizen Lab Traces Zero-Click Candiru Spyware Infections at Al Jazeera to Targeted Online Ads

Candiru, an Israeli maker of spyware sold to governments, infected devices at the news network Al Jazeera through ordinary online ads, in attacks that needed no click or other action from the user, researchers at the Citizen Lab said Thursday. The hidden attack code ran the moment an ad loaded on the screen, and in some cases the ad loaded out of sight, in t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA Adds One Known Exploited Vulnerability to Catalog Critical CISA Advisory
2026-10-15 CISA Advisory

CISA Adds One Known Exploited Vulnerability to Catalog

CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2026-21589 Atlassian Multiple Products Files or Directories Accessible to External Parties Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management requirements for Federal Civilian Executive Branch (FCEB) agencies. BOD 26-04 reinforces the importance of the KEV Catalog and requires federal agencies to prioritize rapid remediation of high-risk vulnerabilities, specifically those identified by Common Vulnerabilities and Exposures (CVEs) listed in CISA’s KEV Catalog on publicly exposed assets that grant total control of the asset post-exploitation, while deferring action for lower-risk vulnerabilities. BOD 26-04 further establishes basic expectations for when agencies must check whether threat actors compromised the system before the patch was applied. While BOD 26-04 applies only to FCEB agencies, CISA encourages all organizations to adopt risk-based vulnerability management and prioritize remediation of KEV Catalog vulnerabilities . CISA will continue to add vulnerabilities to the catalog that meet the specified criteria . Aware of an exploited vulnerability not currently listed in the KEV Catalog? Submit it for potential addition through CISA’s KEV Nomination Form . Potential KEV additions must have a CVE ID, evidence of exploitation, and clear mitigation guidance.

Fix: Review CISA guidance and apply vendor security updates immediately.
Cisco Urges Customers to Patch Email Gateway Flaw and Check for Compromise Important CVE-2026-76519 SecurityAffairs
2026-10-15 SecurityAffairs

Cisco Urges Customers to Patch Email Gateway Flaw and Check for Compromise

Attackers exploit a critical Cisco email gateway flaw to gain root access. Cisco urges customers to update scanner tools and check for compromise. Cisco confirmed this week that threat actors are exploiting a critical vulnerability in Cisco Secure Email Gateway, tracked as CVE-2026-76519 with a CVSS score of 9.8. An attacker can exploit the flaw by sending a…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Palo Alto Networks warns of PAN-OS RCE flaw exploited in attacks Critical CVE-2026-0322 BleepingComputer
2026-10-14 BleepingComputer

Palo Alto Networks warns of PAN-OS RCE flaw exploited in attacks

Palo Alto Networks has released security updates for a high-severity PAN-OS RCE zero-day, tracked as CVE-2026-0322, that has been exploited in attacks targeting firewalls. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Ivanti ICS Zero-Day Attacks Highlight Vendor Patching Hurdles Critical CVE-2026-104935 Dark Reading
2026-10-14 Dark Reading

Ivanti ICS Zero-Day Attacks Highlight Vendor Patching Hurdles

CVE-2026-104935, a high-severity authentication bypass + RCE vulnerability, was only partially discovered and patched in July, leaving an opening for threat actors to capitalize on.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
U.S. CISA adds Microsoft Windows Shell flaw to its Known Exploited Vulnerabilities catalog Important CVE-2026-96951 SecurityAffairs
2026-10-14 SecurityAffairs

U.S. CISA adds Microsoft Windows Shell flaw to its Known Exploited Vulnerabilities catalog

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft Windows Shell flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Microsoft Windows Shell flaw, tracked as CVE-2026-96951 (CVSS score of 8.8), to its Known Exploited Vulnerabilities (KEV) catalog . Microsoft Pa…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Anthropic 'SneakPeek' Flaw Is a Silent Zero-Click Threat Critical Dark Reading
2026-10-14 Dark Reading

Anthropic 'SneakPeek' Flaw Is a Silent Zero-Click Threat

A bug in Claude Code Desktop's preview pane can allow adversaries to quietly steal credentials from developers, including SSH private keys, AWS credentials, and Claude 0Auth tokens.

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cisco patches new Secure Email Gateway zero-day exploited in attacks Critical BleepingComputer
2026-10-14 BleepingComputer

Cisco patches new Secure Email Gateway zero-day exploited in attacks

Cisco has patched another actively exploited zero-day flaw in its Secure Email Gateway (SEG) that lets remote unauthenticated attackers execute commands with root privileges. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Patch Tuesday Sets New Record with 1,415 CVEs in October 2026 Updates Critical CVE-2026-96951 SecurityAffairs
2026-10-14 SecurityAffairs

Microsoft Patch Tuesday Sets New Record with 1,415 CVEs in October 2026 Updates

Microsoft Patch Tuesday security updates for October 2026 address a record 1,415 vulnerabilities. Prioritize the exploited zero-day, critical bugs and potentially wormable vulnerabilities. Microsoft just shattered every patch record in the book. October 2026 brought us a staggering 1,415 new CVEs from Microsoft alone. “Well, it’s a new record release from Mi…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA warns admins to immediately fix Ivanti flaw exploited as zero-day Critical BleepingComputer
2026-10-14 BleepingComputer

CISA warns admins to immediately fix Ivanti flaw exploited as zero-day

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) urged security teams to immediately patch an Ivanti Connect Secure (ICS) flaw exploited in zero-day attacks since at least October 1st. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
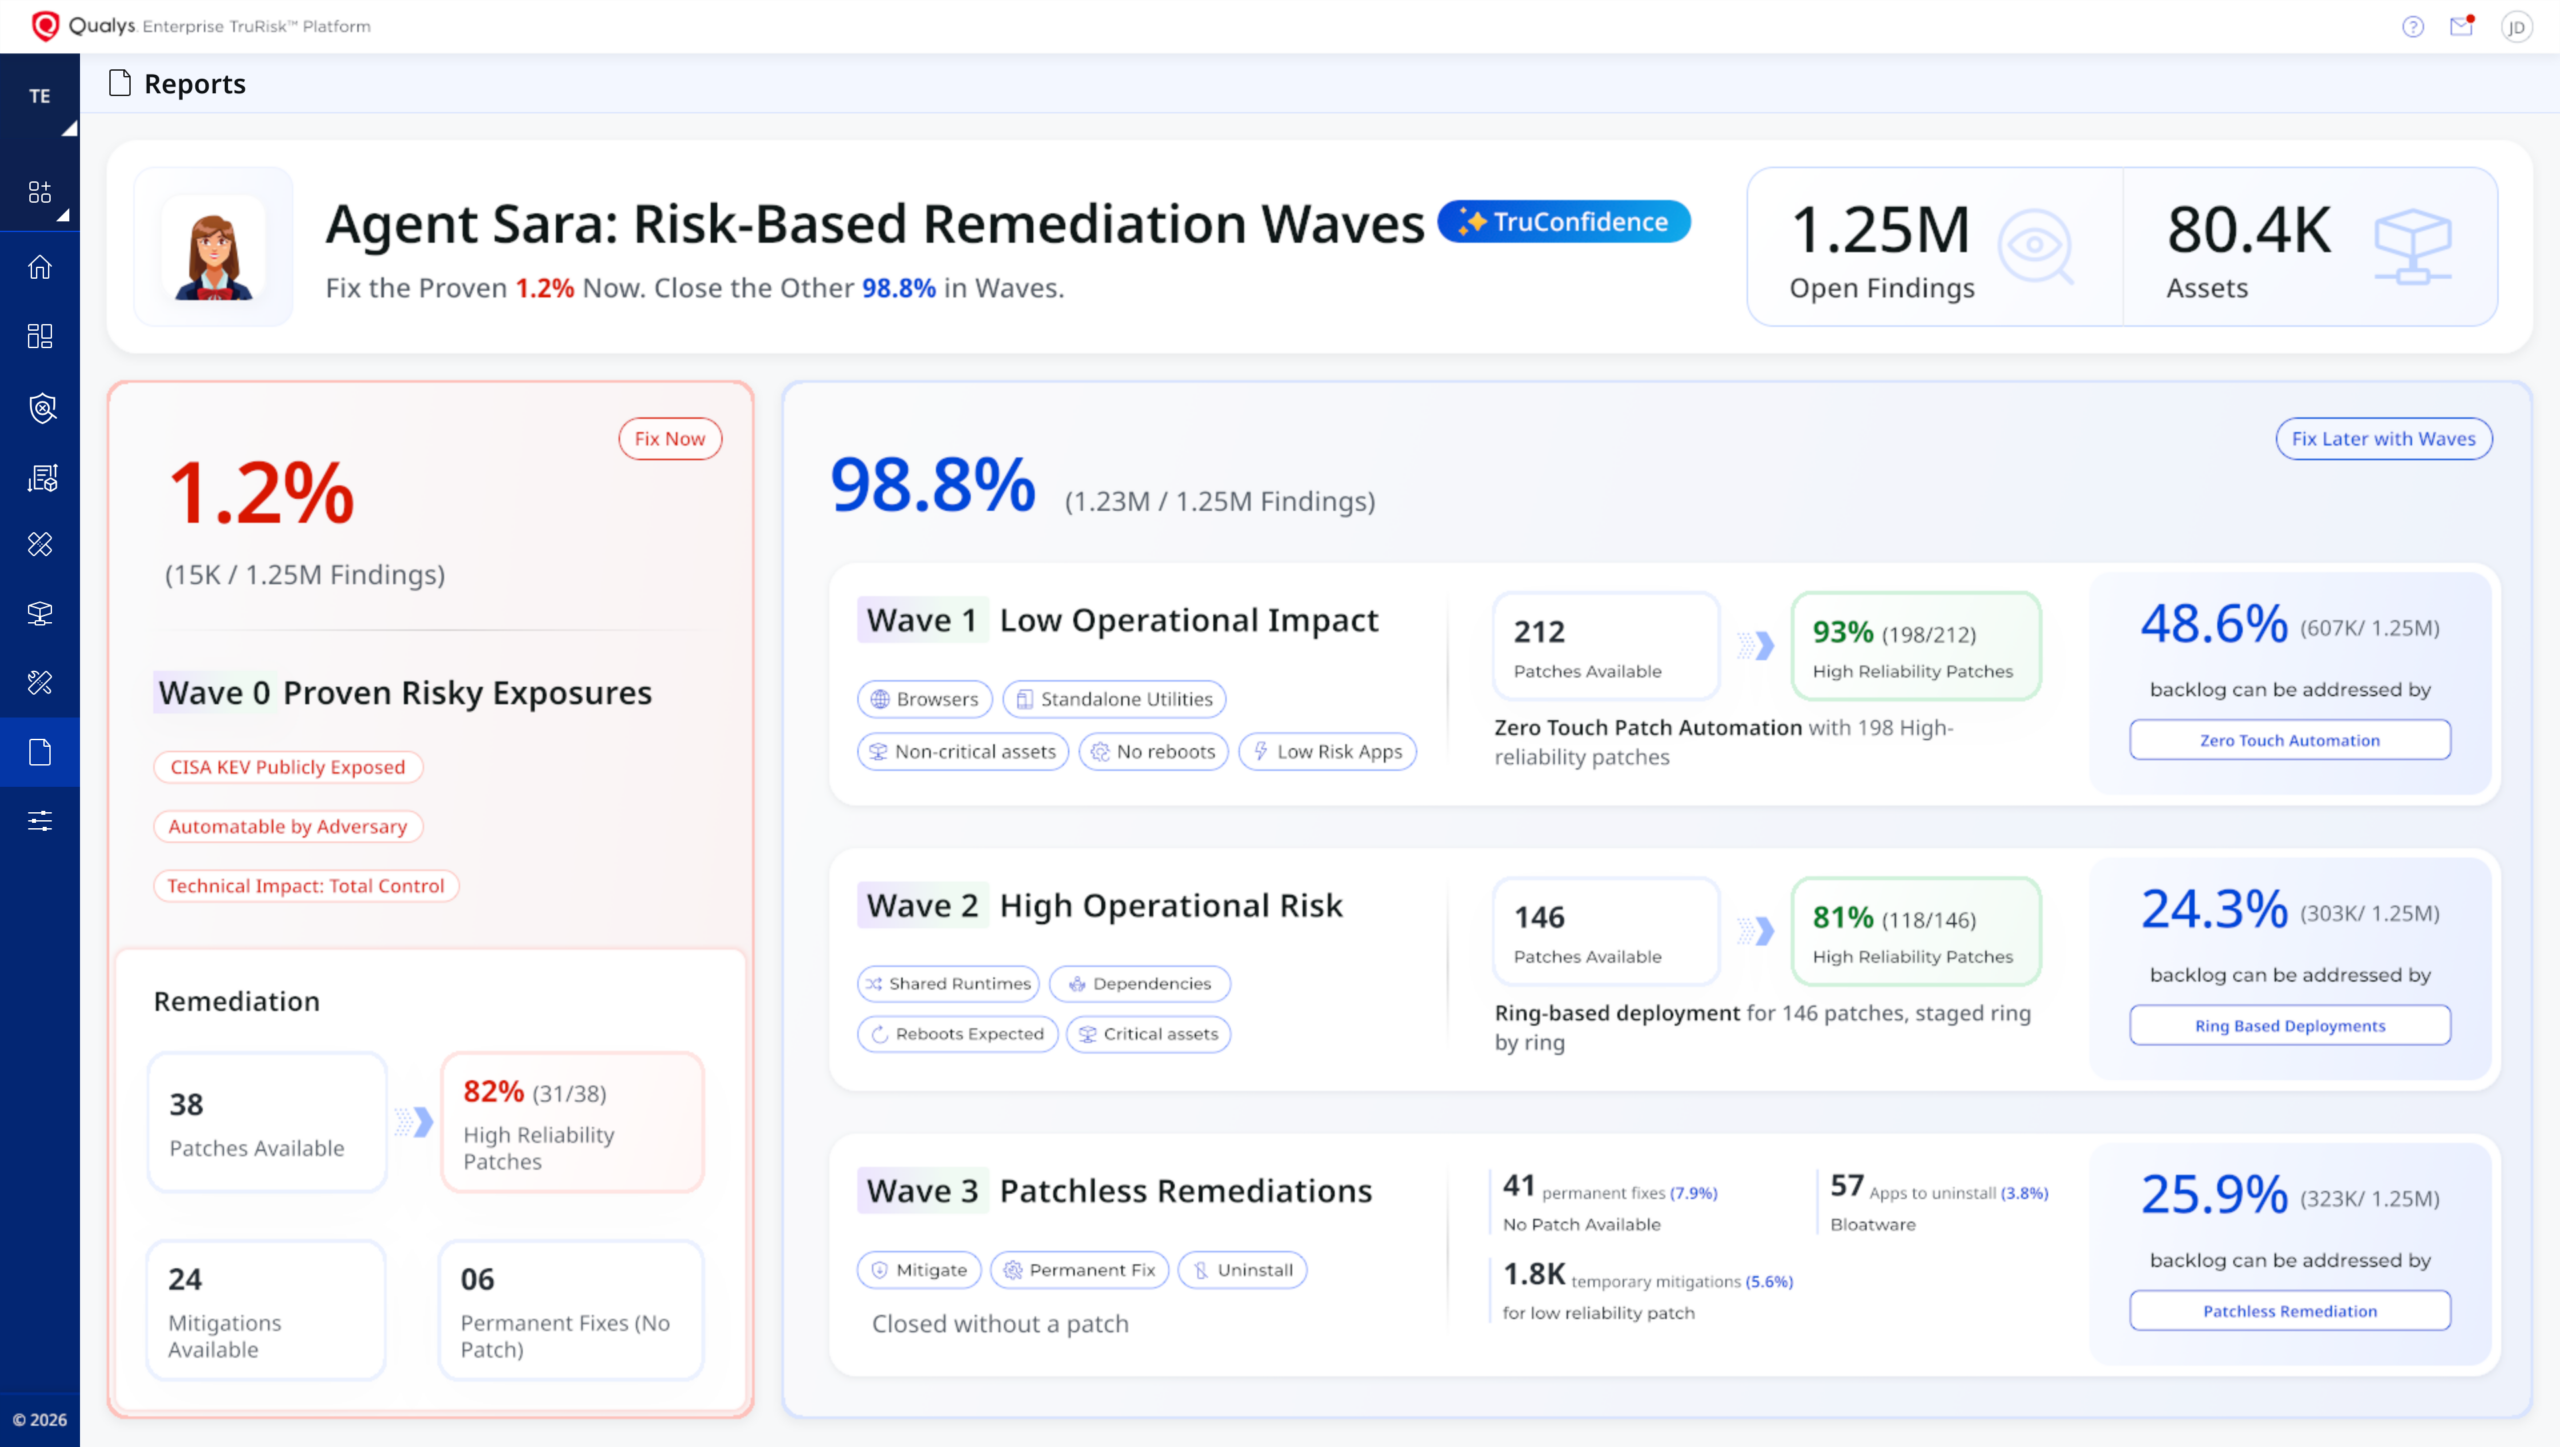
TruConfidence: Why Your Patch Automation Can Finally Be Autonomous Critical Qualys Security Blog
2026-10-14 Qualys Security Blog

TruConfidence: Why Your Patch Automation Can Finally Be Autonomous

TruConfidence: The AI-Powered Remediation Intelligence & Orchestration engine powering TruRisk Eliminate 2.0 delivers autonomous remediation at scale with proof at every step. Executive Summary Vulnerabilities are now discovered faster than enterprises can remediate them. Patch automation has been around for years, but vulnerability backlogs are still growin…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA Urges Immediate Ivanti Connect Secure Updates as Honeypots Log 105 Exploit Attempts Critical CVE-2026-104935 The Hacker News
2026-10-14 The Hacker News

CISA Urges Immediate Ivanti Connect Secure Updates as Honeypots Log 105 Exploit Attempts

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday urged organizations to take steps to immediately update their Ivanti Connect Secure (ICS) appliances and deployments to the latest version following the disclosure of an actively exploited vulnerability. The security flaw, tracked as CVE-2026-104935 (CVSS score: 8.6), is a case of au…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification