Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 608 advisories
Page 4 of 26
CISA Adds Four Known Exploited Vulnerabilities to Catalog Critical CISA Advisory
2026-10-14 CISA Advisory

CISA Adds Four Known Exploited Vulnerabilities to Catalog

CISA has added four new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2026-0322 Palo Alto Networks PAN-OS Code Injection Vulnerability CVE-2026-76519 Cisco Secure Email Gateway Relative Path Traversal Vulnerability CVE-2026-105133 Ahsay AhsayCBS Improper Authentication Vulnerability CVE-2026-105134 Ahsay AhsayCBS Command Injection Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management requirements for Federal Civilian Executive Branch (FCEB) agencies. BOD 26-04 reinforces the importance of the KEV Catalog and requires federal agencies to prioritize rapid remediation of high-risk vulnerabilities, specifically those identified by Common Vulnerabilities and Exposures (CVEs) listed in CISA’s KEV Catalog on publicly exposed assets that grant total control of the asset post-exploitation, while deferring action for lower-risk vulnerabilities. BOD 26-04 further establishes basic expectations for when agencies must check whether threat actors compromised the system before the patch was applied. While BOD 26-04 applies only to FCEB agencies, CISA encourages all organizations to adopt risk-based vulnerability management and prioritize remediation of KEV Catalog vulnerabilities . CISA will continue to add vulnerabilities to the catalog that meet the specified criteria . Aware of an exploited vulnerability not currently listed in the KEV Catalog? Submit it for potential addition through CISA’s KEV Nomination Form . Potential KEV additions must have a CVE ID, evidence of exploitation, and clear mitigation guidance.
Fix: Review CISA guidance and apply vendor security updates immediately.
Update Windows: Record Patch Tuesday fixes flaw already under attack Critical CVE-2026-96951 Malwarebytes Labs
2026-10-14 Malwarebytes Labs

Update Windows: Record Patch Tuesday fixes flaw already under attack

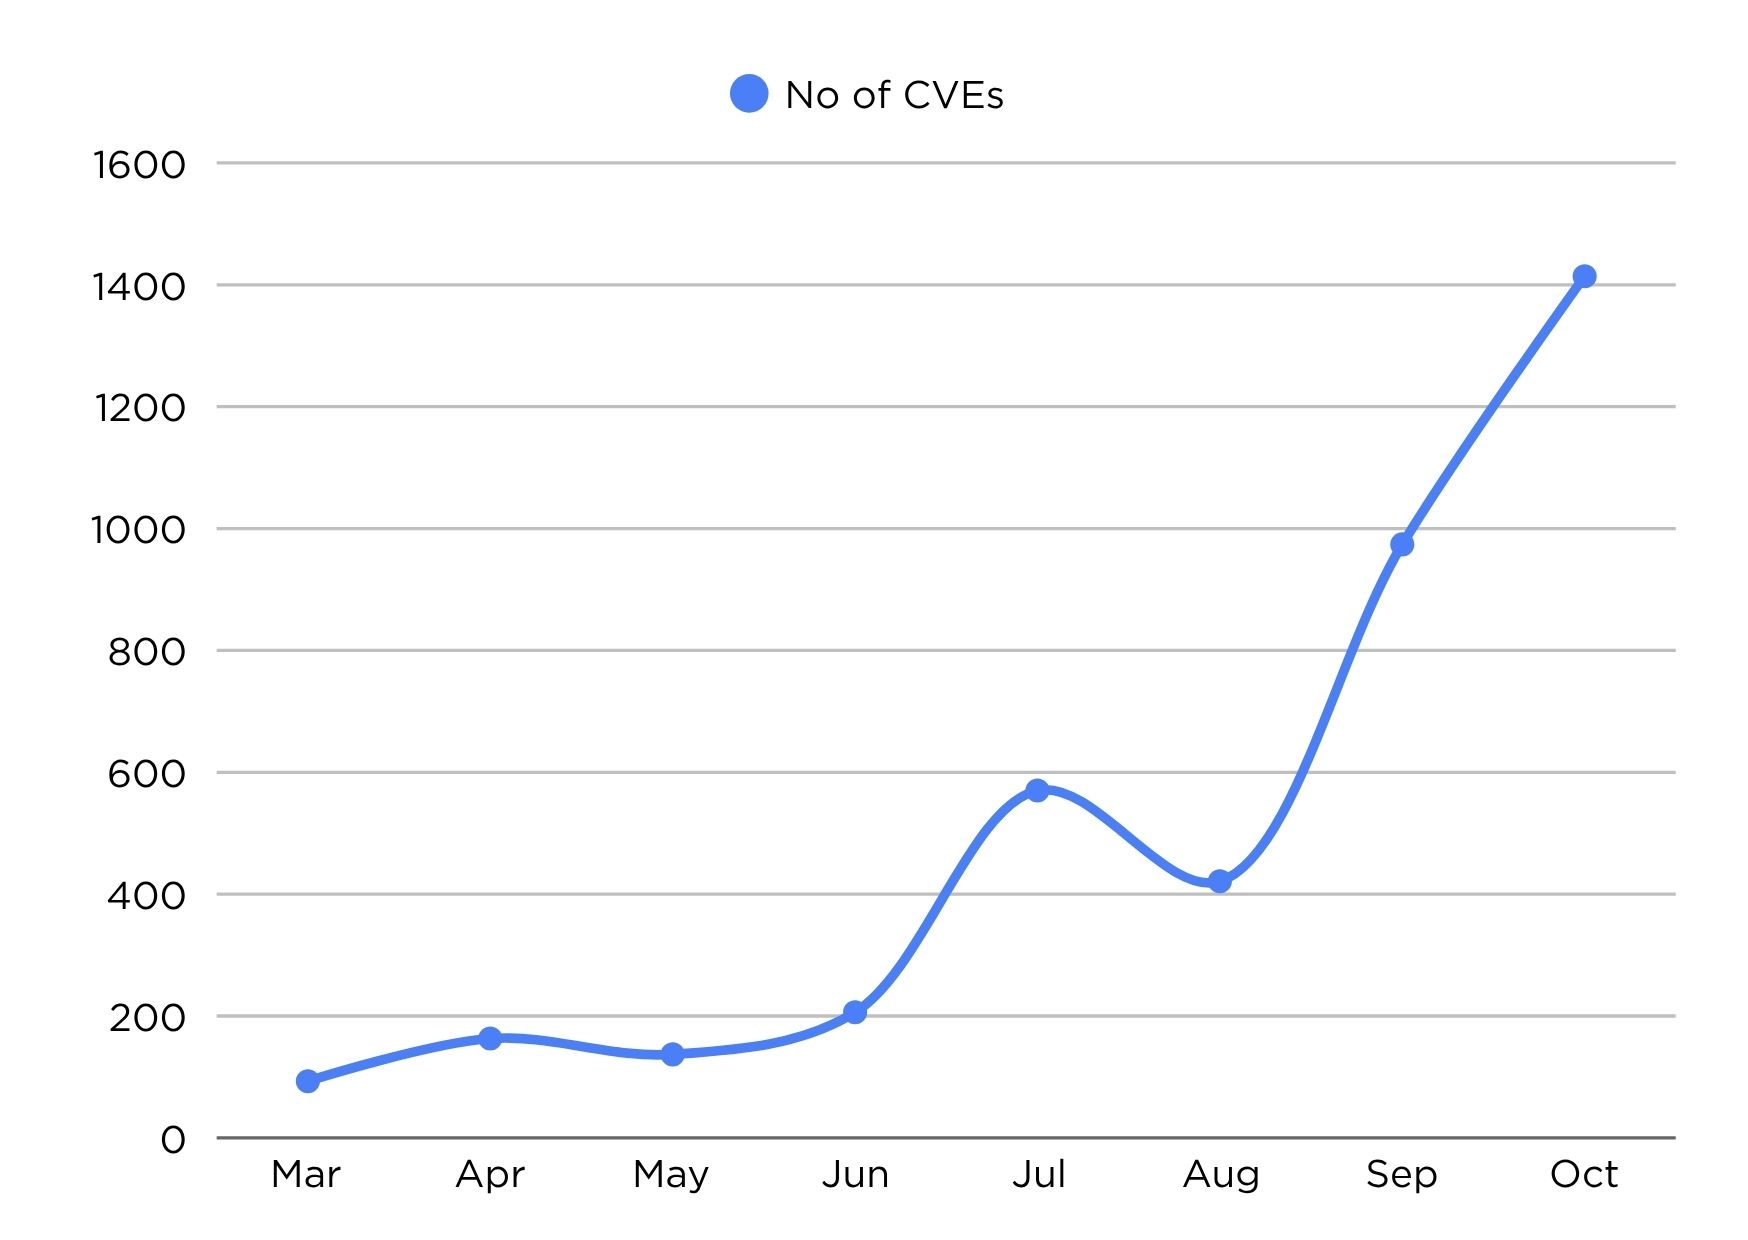
Microsoft’s October Patch Tuesday release addresses a record-breaking 1,413 vulnerabilities , including an actively exploited Windows Shell zero-day and two other publicly disclosed flaws. Just when you thought a previous record would stand for a while, Microsoft comes out again with the largest monthly Patch Tuesday release. Microsoft has said its growing u…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Volexity Uncovers Stealthy Ivanti VPN Attack Using Three Zero-Day Vulnerabilities Critical CVE-2026-104935 SecurityAffairs
2026-10-14 SecurityAffairs

Volexity Uncovers Stealthy Ivanti VPN Attack Using Three Zero-Day Vulnerabilities

Ivanti VPN zero-days let attackers gain root access, steal credentials, evade detection, and prepare for wider network compromise. On October 5, Volexity started investigating suspicious activity at one of its monitoring customers and traced everything back to an Ivanti Connect Secure VPN appliance running version 22.8R2.4, the latest build available at the …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Attackers chained three Ivanti zero-days to gain root on fully patched VPN appliances Critical Help Net Security
2026-10-14 Help Net Security

Attackers chained three Ivanti zero-days to gain root on fully patched VPN appliances

A threat actor has been using an exploit chain combining three vulnerabilities in Ivanti’s Connect Secure (ICS) appliances to breach organizations, collect credentials, exfiltrate configuration data, and perform network reconnaissance. “In the first week of October 2026, Volexity discovered an unknown threat actor, UTA0576, abusing a zero-day exploit chain t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft fixes exploited Mark of the Web bypass vulnerability (CVE-2026-96951) Critical CVE-2026-96951 Help Net Security
2026-10-14 Help Net Security

Microsoft fixes exploited Mark of the Web bypass vulnerability (CVE-2026-96951)

In another record-breaking Patch Tuesday, Microsoft has squashed over 1,400 security bugs, including a Mark of the Web bypass vulnerability (CVE-2026-96951) exploited by attackers in the wild. CVE-2026-96951 is a command injection vulnerability in Windows Shell that can be triggered by remote attackers via a file that is designed to exploit the vulnerability…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How a leaked builder of XWorm turned a remote access trojan into a surveillance kit Critical SecurityAffairs
2026-10-14 SecurityAffairs

How a leaked builder of XWorm turned a remote access trojan into a surveillance kit

Netskope tracks four XWorm versions in the wild, 46 plugins, and new tools for location, audio and live browser control, with detections up fourfold. Netskope Threat Labs has been following XWorm since September 2024, and its latest report shows the malware has changed a lot. Over the past year the team identified four distinct versions running at the same t…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Patch Tuesday - October 2026 Moderate CVE-2026-96951 Rapid7 Threat Research
2026-10-13 Rapid7 Threat Research

Patch Tuesday - October 2026

Microsoft is publishing 1,413 own-product vulnerabilities on October 2026 Patch Tuesday , including 1,102 vulnerabilities in Windows. Anyone who enjoyed last month’s record-setting Patch Tuesday will love the October 2026 edition, because it’s much bigger still. As Rapid7 has noted over the course of 2026, there is every reason to suppose that vulnerability …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Patch Tuesday, October 2026 Security Update Review Critical CVE-2026-96951 Qualys Security Blog
2026-10-13 Qualys Security Blog

Microsoft Patch Tuesday, October 2026 Security Update Review

Microsoft has released its October 2026 Patch Tuesday security updates, addressing vulnerabilities across its products and services. As organizations continue to navigate an evolving threat landscape, applying security patches promptly remains critical to reducing exposure and strengthening security posture. This month’s updates highlight the importance of i…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Patch Tuesday for October 2026 — Snort rules and prominent vulnerabilities Critical CVE-2026-96951 Cisco Talos Intelligence
2026-10-13 Cisco Talos Intelligence

Microsoft Patch Tuesday for October 2026 — Snort rules and prominent vulnerabilities

Microsoft has released its monthly security update for October 2026, which includes 1415 vulnerabilities affecting a range of products, including 85 that Microsoft marked as "critical." Microsoft notes that 1 of the vulnerabilities disclosed this month have been exploited in the wild CVE-2026-96951 is a security feature bypass vulnerability that affects Wind…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft October 2026 Patch Tuesday fixes 1,411 flaws, 3 zero-days Critical BleepingComputer
2026-10-13 BleepingComputer

Microsoft October 2026 Patch Tuesday fixes 1,411 flaws, 3 zero-days

Today is Microsoft's October 2026 Patch Tuesday, with security updates addressing a record-breaking 1,411 flaws, including one actively exploited and two publicly disclosed zero-day vulnerabilities. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The October 2026 Security Update Review Critical CVE-2026-75650 Trend Micro ZDI
2026-10-13 Trend Micro ZDI

The October 2026 Security Update Review

Another month of patches equals another new record for Microsoft patches. It’s a good thing I survive Pwn2Own Ireland , because between these and the Adobe patches, there’s much to discuss. I’m also looking at different ways I can represent the bugs at this level of volume, so let me know if you have ideas. (Seriously – I’m out of ideas). If you’d rather wat…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
U.S. CISA adds Ivanti Connect Secure flaw to its Known Exploited Vulnerabilities catalog Important CVE-2026-104935 SecurityAffairs
2026-10-13 SecurityAffairs

U.S. CISA adds Ivanti Connect Secure flaw to its Known Exploited Vulnerabilities catalog

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Ivanti Connect Secure flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Ivanti Connect Secure FortiMail flaw, tracked as CVE-2026-104935 (CVSS score of 8.6), to its Known Exploited Vulnerabilities (KEV) catalog . The …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Attacker Chains Three Ivanti Connect Secure Zero-Days for Root Access, Only Two Patched So Far Critical The Hacker News
2026-10-13 The Hacker News

Attacker Chains Three Ivanti Connect Secure Zero-Days for Root Access, Only Two Patched So Far

An attacker chained three zero-day flaws in Ivanti Connect Secure, a VPN appliance, to run commands as root without logging in, security firm Volexity said on October 13. Ivanti has released fixes for two of the flaws and told customers on affected versions to "act immediately." A fix for the third is still pending, according to Volexity. Volexity, which rep…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Ivanti Connect Secure zero-day exploited in the wild (CVE-2026-104935) Critical CVE-2026-104935 Rapid7 Threat Research
2026-10-13 Rapid7 Threat Research

Ivanti Connect Secure zero-day exploited in the wild (CVE-2026-104935)

Overview On October 13, 2026, Ivanti published a security advisory for CVE-2026-104935 , a high-severity authentication bypass by spoofing ( CWE-290 ) affecting Ivanti Connect Secure (ICS). The vulnerability has a CVSSv3.0 score of 8.6 and allows a remote, unauthenticated attacker to execute arbitrary commands. Ivanti reports that exploitation in the wild ha…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Ivanti warns of Connect Secure zero-day exploited in attacks Critical BleepingComputer
2026-10-13 BleepingComputer

Ivanti warns of Connect Secure zero-day exploited in attacks

Ivanti urged customers on Tuesday to immediately patch an actively exploited zero-day vulnerability in the Ivanti Connect Secure (ICS) remote access gateway. [...]

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CISA Adds Two Known Exploited Vulnerabilities to Catalog Critical CISA Advisory
2026-10-13 CISA Advisory

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2026-96951 Microsoft Windows Command Injection Vulnerability CVE-2026-104935 Ivanti Connect Secure Authentication Bypass by Spoofing Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management requirements for Federal Civilian Executive Branch (FCEB) agencies. BOD 26-04 reinforces the importance of the KEV Catalog and requires federal agencies to prioritize rapid remediation of high-risk vulnerabilities, specifically those identified by Common Vulnerabilities and Exposures (CVEs) listed in CISA’s KEV Catalog on publicly exposed assets that grant total control of the asset post-exploitation, while deferring action for lower-risk vulnerabilities. BOD 26-04 further establishes basic expectations for when agencies must check whether threat actors compromised the system before the patch was applied. While BOD 26-04 applies only to FCEB agencies, CISA encourages all organizations to adopt risk-based vulnerability management and prioritize remediation of KEV Catalog vulnerabilities . CISA will continue to add vulnerabilities to the catalog that meet the specified criteria . Aware of an exploited vulnerability not currently listed in the KEV Catalog? Submit it for potential addition through CISA’s KEV Nomination Form . Potential KEV additions must have a CVE ID, evidence of exploitation, and clear mitigation guidance.
Fix: Review CISA guidance and apply vendor security updates immediately.
CISA Urges Patching Newly Exploited Vulnerability in Ivanti Connect Secure Critical CISA Advisory
2026-10-13 CISA Advisory

CISA Urges Patching Newly Exploited Vulnerability in Ivanti Connect Secure

CISA is aware of Ivanti’s disclosure of a newly exploited vulnerability, CVE-2026-104935 , affecting Ivanti Connect Secure versions 25.1.1.1 and prior, 25.1.2.2 and prior, and 22.8R2.4 and prior. CISA is aware of cyber threat actors exploiting this zero-day authentication bypass vulnerability, which allows remote, unauthenticated execution of arbitrary commands, to conduct credential theft and data exfiltration. CISA added CVE-2026-104935 to its Known Exploited Vulnerabilities (KEV) Catalog on Oct. 13, 2026. CISA urges organizations with affected Ivanti Connect Secure appliances and deployments to immediately update to the latest version, as outlined in Ivanti’s Security Advisory Ivanti Connect Secure (CVE-2026-104935) . Organizations should also review the Ivanti Connect Secure 25.x Upgrade and Migration Compatibility Guide for detailed patching guidance for hardware and virtual appliance deployments. Ivanti Connect Secure version 22.8 reaches end of life on Jan. 31, 2027. Organizations seeking to determine whether they were compromised will need to conduct network and memory forensics to identify evidence of exploitation. Note: Ivanti’s Integrity Checker Tool may not detect evidence of exploitation of CVE-2026-104935 because threat actor commands execute in memory. If your organization suspects a compromise, CISA recommends implementing the following actions from Ivanti Connect Secure Recovery Procedures : Create a backup of the appliance configuration. Review Ivanti’s How to Backup & Restore the Binary Configuration Using Archiving Server for more information. Conduct a factory reset and upgrade the appliance to the latest version. For cloud and virtual systems, rebuild the virtual instance and upgrade to the latest version. Restore the appliance configuration from the backup created in step 1. Reset passwords for all accounts, including domain, administrator, and local accounts. Revoke and reissue stored certificates; reset stored API keys and license server credentials. CISA urges organizations to review the Ivanti security advisory and guide noted above and apply necessary updates. CISA also recommends reviewing the Volexity blog, A Series of Unauthenticated Events: Chained Exploitation of Ivanti Connect Secure Zero-Days . Disclaimer The information in this report is being provided “as is” for informational purposes only. CISA does not endorse any commercial entity, product, company, or service, including any entities, products, or services linked within this document. Any reference to specific commercial entities, products, processes, or services by service mark, trademark, manufacturer, or otherwise, does not constitute or imply endorsement, recommendation, or favoring by CISA.

Fix: Review CISA guidance and apply vendor security updates immediately.
ShinyHunters arrest number three: a Canadian ransomware negotiator Critical SecurityAffairs
2026-10-12 SecurityAffairs

ShinyHunters arrest number three: a Canadian ransomware negotiator

A Canadian ransomware negotiator faces extortion charges in the FBI’s ShinyHunters crackdown. Here’s what is known, and what isn’t. ShinyHunters is the focus of a global FBI investigation, and the crackdown has led to the October 8 arrest of a Canadian ransomware negotiator who now faces extortion charges. Reuters reported the arrest, citing court documents,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
⚡ Weekly Recap: Helpdesk 0-Days, Rogue Certs, ShinyHunters Arrest, AI-Fooling Malware and More Critical The Hacker News
2026-10-12 The Hacker News

⚡ Weekly Recap: Helpdesk 0-Days, Rogue Certs, ShinyHunters Arrest, AI-Fooling Malware and More

Some meetings last longer than it took attackers to jump on a newly disclosed security flaw this week. Within hours, they were already testing it. That's not much time to read the warning, let alone do something about it. But speed is only part of the problem. A secure connection didn't always mean a safe destination. People offering to fix a ransomware mess…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Exploitability Needs Runtime Evidence: Understanding Runtime Vulnerability Reachability for Containers Important Qualys Security Blog
2026-10-12 Qualys Security Blog

Exploitability Needs Runtime Evidence: Understanding Runtime Vulnerability Reachability for Containers

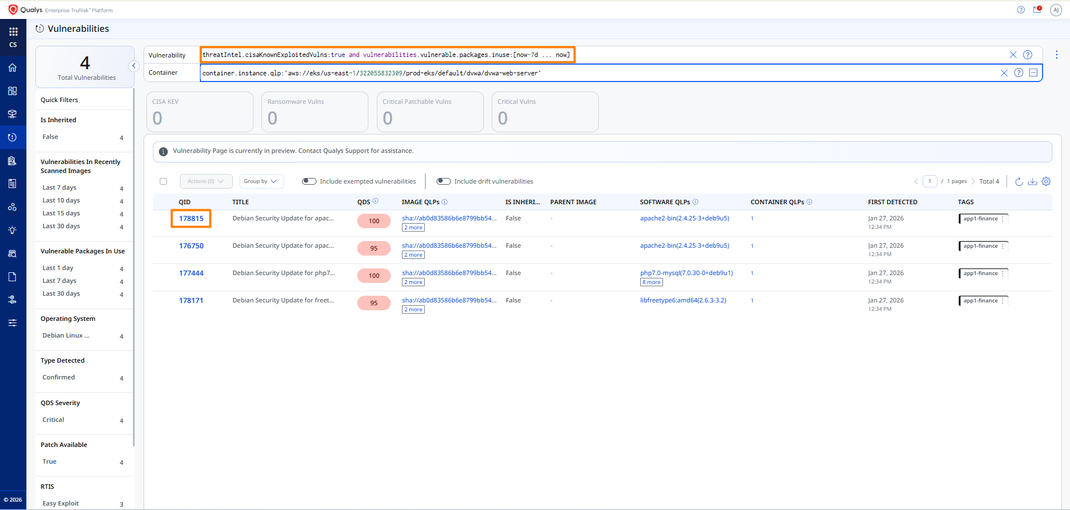
Key Takeaways Qualys Runtime Vulnerability Reachability for Containers brings runtime evidence directly into vulnerability prioritization. Package presence in a container image does not mean the vulnerable software is actually part of the workload’s live execution. Runtime reachability answers whether the vulnerable software is relevant to a running workload…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
SonicWall Patches CVSS 10.0 SSRF Flaw as Attacks Begin Critical CVE-2026-102255 SecurityAffairs
2026-10-12 SecurityAffairs

SonicWall Patches CVSS 10.0 SSRF Flaw as Attacks Begin

Attackers are exploiting SonicWall SMA 1000 vulnerability, tracked as CVE-2026-102255 (CVSS score of 10.0), just days after its public disclosure. Attackers have begun exploiting a critical flaw in SonicWall SMA 1000 appliances, tracked as CVE-2026-102255 (CVSS score of 10.0), just days after public disclosure. The vulnerability is a server-side request forg…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Attackers Exploit CVSS 10.0 Bricksforge WordPress Flaw Enabling Unauthenticated RCE Critical CVE-2026-85097 The Hacker News
2026-10-12 The Hacker News

Attackers Exploit CVSS 10.0 Bricksforge WordPress Flaw Enabling Unauthenticated RCE

A maximum-severity security flaw impacting the Bricksforge plugin for WordPress has come under active exploitation in the wild, according to Patchstack. The critical vulnerability in question is CVE-2026-85097 (CVSS score: 10.0), which allows unauthenticated attackers to upload and execute arbitrary PHP code on vulnerable WordPress websites, resulting in rem…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Let’s Encrypt TLS certificate lifetimes to drop from 90 to 64 days starting February 2027 Moderate Help Net Security
2026-10-12 Help Net Security

Let’s Encrypt TLS certificate lifetimes to drop from 90 to 64 days starting February 2027

Websites that rely on Let’s Encrypt will soon have to renew their TLS certificates more often. Starting February 10, 2027, the certificate authority will issue certificates valid for 64 days by default, down from 90 days. Subscribers who already use Let’s Encrypt’s optional 45-day or 6-day certificates are not affected. The organization expects the last 90-d…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification