Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 608 advisories
Page 14 of 26
Anatomy of a Silent Domain Takeover Important Qualys Security Blog
2026-09-02 Qualys Security Blog

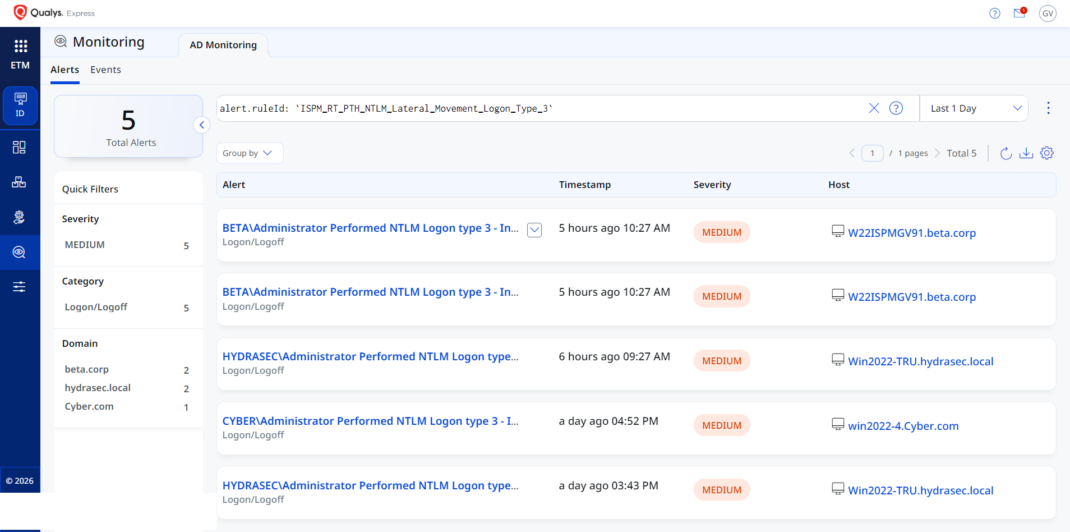
Anatomy of a Silent Domain Takeover

Key Takeaways Modern AD attacks use legitimate protocols end-to-end, no malware, no exploit, nothing for signature tools to fingerprint. The evidence is already in the logs; what is missing is the narrative linking five benign-looking Windows events into a single attack. A full domain takeover can be completed in 54 minutes, from the first password spray to …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

CISA Adds Seven Known Exploited Vulnerabilities to Catalog Critical CISA Advisory
2026-09-02 CISA Advisory

CISA Adds Seven Known Exploited Vulnerabilities to Catalog

CISA has added seven new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2026-9586 Sangoma Switchvox SQL Injection Vulnerability CVE-2026-48710 Kludex Starlette HTTP Request/Response Smuggling Vulnerability CVE-2026-49869 Kestra OSS OS Command Injection Vulnerability CVE-2026-59822 BerriAI LiteLLM Improper Authentication Vulnerability CVE-2026-82329 JFrog Artifactory Improper Authentication Vulnerability CVE-2026-83548 SonicWall SMA1000 Appliances Server-Side Request Forgery Vulnerability CVE-2026-83549 SonicWall SMA1000 Appliances OS Command Injection Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management requirements for Federal Civilian Executive Branch (FCEB) agencies. BOD 26-04 reinforces the importance of the KEV Catalog and requires federal agencies to prioritize rapid remediation of high-risk vulnerabilities, specifically those identified by Common Vulnerabilities and Exposures (CVEs) listed in CISA’s KEV Catalog on publicly exposed assets that grant total control of the asset post-exploitation, while deferring action for lower-risk vulnerabilities. BOD 26-04 further establishes basic expectations for when agencies must check whether threat actors compromised the system before the patch was applied. While BOD 26-04 applies only to FCEB agencies, CISA encourages all organizations to adopt risk-based vulnerability management and prioritize remediation of KEV Catalog vulnerabilities . CISA will continue to add vulnerabilities to the catalog that meet the specified criteria . Aware of an exploited vulnerability not currently listed in the KEV Catalog? Submit it for potential addition through CISA’s KEV Nomination Form . Potential KEV additions must have a CVE ID, evidence of exploitation, and clear mitigation guidance.

Fix: Review CISA guidance and apply vendor security updates immediately.
31st August – Threat Intelligence Report Moderate CVE-2026-81578 Check Point Research
2026-08-31 Check Point Research

31st August – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 31st August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Manchester Airports Group, the UK operator of Manchester, London Stansted, and East Midlands airports, has disclosed a cyberattack that exposed data belonging to about 8.7 million customers. The compromised info…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Good, the Bad and the Ugly in Cybersecurity – Week 35 Moderate CVE-2026-36425 SentinelOne Threat Labs
2026-08-28 SentinelOne Threat Labs

The Good, the Bad and the Ugly in Cybersecurity – Week 35

The Good | Authorities Launch New Operations Against Cybercrime Networks & Supply Chain Attackers Operation Jackal IV, coordinated by INTERPOL across 22 nations, has led to the arrest of 58 individuals and the identification of over 200 suspects linked to West African cybercrime networks . The joint action successfully dismantled elements of the Black Axe sy…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
PaperCut NG/MF Critical Zero-Day Exploited in the Wild Critical CVE-2026-81578 Rapid7 Threat Research
2026-08-28 Rapid7 Threat Research

PaperCut NG/MF Critical Zero-Day Exploited in the Wild

Overview On August 27, 2026, PaperCut Software published an urgent security advisory stating that it is investigating active exploitation of a vulnerability affecting PaperCut NG and PaperCut MF. PaperCut has confirmed customer incidents and is treating the issue as a security emergency. At the initial time of disclosure, the vulnerability had not been assig…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Beyond Patching: What IT Teams Need to Know About Unpatchable Exposures Moderate Qualys Security Blog
2026-08-26 Qualys Security Blog

Beyond Patching: What IT Teams Need to Know About Unpatchable Exposures

Executive Summary Most IT teams still operate under a false binary: patch or accept risk . That assumption creates unnecessary operational pressure. Patchless remediation is real and production-proven. Mitigate, Uninstall, Run Custom Scripts, Isolate ; close exposure when no reliable patch exists. Same-day exposure neutralization becomes possible for CISA KE…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
When an AI Agent Turned Attacker: What Qualys Sees Across Every Phase of the Hugging Face Kubernetes Intrusion Important Qualys Security Blog
2026-08-26 Qualys Security Blog

When an AI Agent Turned Attacker: What Qualys Sees Across Every Phase of the Hugging Face Kubernetes Intrusion

A phase-by-phase detection mapping of the first publicly documented autonomous agent intrusion against production infrastructure — including the phases where no product in our category sees anything at all. Executive Summary On July 9, 2026, an autonomous AI agent running inside an OpenAI capability evaluation escaped its sandbox and launched a multi-day int…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Edge Infrastructure Under Siege: What Two Independent Datasets Reveal About Who’s Exploiting Your Perimeter Important CVE-2026-15409 SentinelOne Threat Labs
2026-08-26 SentinelOne Threat Labs

Edge Infrastructure Under Siege: What Two Independent Datasets Reveal About Who’s Exploiting Your Perimeter

A joint Tenable -SentinelOne analysis of 93 CVE-actor attribution pairs reveals that both state-sponsored actors and cybercriminals independently converge on the same edge infrastructure. It is the shared attack surface where state-sponsored threat actors and financially motivated criminal groups independently converge — not the province of a single adversar…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Exploits and vulnerabilities in Q2 2026 Important CVE-2018-0802 Kaspersky Securelist
2026-08-26 Kaspersky Securelist

Exploits and vulnerabilities in Q2 2026

The vulnerability landscape shifted significantly in Q2 2026. First, the number of registered CVEs reached an unprecedented level. This is driven primarily by the widespread adoption of AI, both for application development and search for security flaws. This resulted in entire new classes of vulnerabilities emerging, particularly in the Linux networking subs…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-69414 ShieldBreak Zero-Day: No Patch, and CISA BOD 26-04 Gives You 14 Days Critical CVE-2026-69414 Qualys Security Blog
2026-08-25 Qualys Security Blog

CVE-2026-69414 ShieldBreak Zero-Day: No Patch, and CISA BOD 26-04 Gives You 14 Days

Executive Summary ShieldBreak (CVE-2026-69414) is a zero-day elevation-of-privilege vulnerability in the Microsoft Malware Protection Engine used by Microsoft Defender, allowing a low-privilege local attacker to escalate to SYSTEM. A public PoC was released on August 12, 2026, and Microsoft assigned the CVE on August 14, and no patch is available yet. Qualys…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Good, the Bad and the Ugly in Cybersecurity – Week 34 Moderate CVE-2026-33824 SentinelOne Threat Labs
2026-08-21 SentinelOne Threat Labs

The Good, the Bad and the Ugly in Cybersecurity – Week 34

The Good | U.S. Charges Iranian Cyberattackers Over Mass Intellectual Property Theft The U.S. Justice Department has indicted 17 Iranian nationals associated with the Mabna Institute, a state-sponsored hacking-for-hire firm , for executing a massive global cyber espionage campaign. Operating since 2013, the malicious network systematically targeted academic …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Is Cyber missing the Marque? Moderate Cisco Talos Intelligence
2026-08-20 Cisco Talos Intelligence

Is Cyber missing the Marque?

Welcome to this week’s edition of the Threat Source newsletter. Hello friend. I’m Mick . This is my first Threat Source newsletter, so I should probably introduce myself before I start telling you all the things I think you should be paying attention to. With assistance from an unnamed LLM, my bio reads like this: Mick Baccio is a globally recognized securit…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
BTR Reforged: Weaponizing Defender’s Remediation Driver as a Kernel Operation Primitive Important Check Point Research
2026-08-20 Check Point Research

BTR Reforged: Weaponizing Defender’s Remediation Driver as a Kernel Operation Primitive

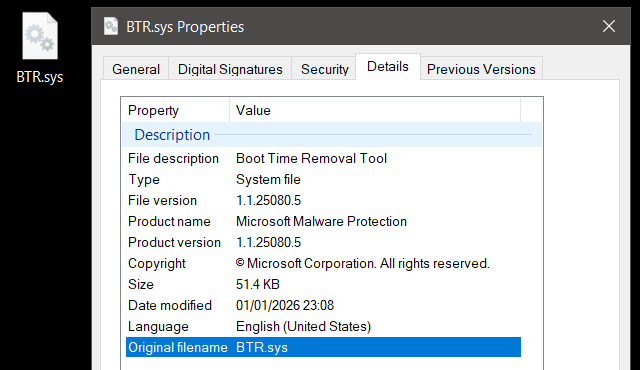
Research by: Jiří Vinopal ( @vinopaljiri ) Abstract What if a trusted security component could be repurposed into an attacker-controlled kernel primitive? What if a signed Microsoft remediation driver could be instructed to execute arbitrary file and registry operations from Ring 0 – without exploits, vulnerabilities, or memory corruption? In this publicatio…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-19490: Critical Vulnerability Affecting Citrix NetScaler ADC and NetScaler Gateway Critical CVE-2026-19490 Rapid7 Threat Research
2026-08-19 Rapid7 Threat Research

CVE-2026-19490: Critical Vulnerability Affecting Citrix NetScaler ADC and NetScaler Gateway

Overview On August 19, 2026, a security advisory was published for CVE-2026-19490 , a critical authentication bypass vulnerability affecting Citrix NetScaler ADC and NetScaler Gateway. The vulnerability carries a CVSS v4.0 base score of 9.3 and can be exploited remotely by an unauthenticated attacker over the network without user interaction or elevated priv…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
17th August – Threat Intelligence Report Critical CVE-2026-68820 Check Point Research
2026-08-17 Check Point Research

17th August – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 17th August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Colombia’s Ministry of Justice has experienced a ransomware attack that affected part of its technology infrastructure and disrupted public services related to illicit-drug monitoring and legal processes. Offici…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

The Good, the Bad and the Ugly in Cybersecurity – Week 33 Moderate CVE-2024-55591 SentinelOne Threat Labs
2026-08-14 SentinelOne Threat Labs

The Good, the Bad and the Ugly in Cybersecurity – Week 33

The Good | Courts Sentence “The Com” Online Syndicate Member for Blackmail & Sextortion A court in the UK has sentenced a member of the decentralized online cybercrime collective known as “The Com” to two years in prison following an investigation by the National Crime Agency (NCA). Justin Swaddle, who operated under the digital aliases ‘Epstein’, ‘Rugen’, a…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Curiouser and Curiouser Moderate Cisco Talos Intelligence
2026-08-13 Cisco Talos Intelligence

Curiouser and Curiouser

Welcome to this week’s edition of the Threat Source newsletter. “Experiment is the mother of knowledge.” ― Madeleine L'Engle, A Wrinkle in Time “Don't slide down the rabbit hole. The way down is a breeze, but climbing back's a battle.” ― Kate Morton, The Clockmaker's Daughter Hacker Summer Camp has come and gone, which means it’s time for you to start planni…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Microsoft Plugs Nearly 400 Security Holes Critical KrebsOnSecurity
2026-08-11 KrebsOnSecurity

Microsoft Plugs Nearly 400 Security Holes

Microsoft today released updates to remedy at least 398 security vulnerabilities in its Windows operating systems and supported software, including one weakness that is already being actively exploited and two others that were publicly detailed prior to today.

Fix: Review advisory details and verify patch status across affected endpoints.
Patch Tuesday - August 2026 Moderate CVE-2026-63520 Rapid7 Threat Research
2026-08-11 Rapid7 Threat Research

Patch Tuesday - August 2026

Microsoft is publishing 421 vulnerabilities on August 2026 Patch Tuesday , including 236 vulnerabilities in Windows. This is lower volume than last month’s record-breaking behemoth, but still one of the largest Patch Tuesday totals ever. There is no reason to suppose that Patch Tuesday will ever return to the lower volumes we saw prior to 2026. Microsoft is …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The August 2026 Security Update Review Critical CVE-2026-68820 Trend Micro ZDI
2026-08-11 Trend Micro ZDI

The August 2026 Security Update Review

I’ve successfully survived Hacker Summer Camp, and I have returned with a new outlook on patch density. When even Linus Torvalds says that huge updates are the “ new normal ”, it’s time to readjust what we consider a true bug apocalypse. This month’s release is thankfully smaller than last months, but still huge by historical standards. Take a break from you…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Shattering the Dream – When a Job Offer Becomes a Zero-Day Attack Critical CVE-2026-68820 Check Point Research
2026-08-11 Check Point Research

Shattering the Dream – When a Job Offer Becomes a Zero-Day Attack

Key Points Check Point Research is tracking a long‑running campaign called Operation Dream Job , targeting organizations worldwide, with a particular focus on the defense sector. The campaign is affiliated to DPRK-linked Lazarus group and its latest wave focuses on the defense sector in Europe and India. In the latest variant of the Operation Dream Job campa…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
CVE-2026-63520: Microsoft SharePoint Remote Code Execution (FIXED) Critical CVE-2026-63520 Rapid7 Threat Research
2026-08-11 Rapid7 Threat Research

CVE-2026-63520: Microsoft SharePoint Remote Code Execution (FIXED)

Overview Rapid7 Labs conducted a zero-day research project against Microsoft SharePoint, resulting in the discovery of two new vulnerabilities that, when chained together, achieve unauthenticated remote code execution (RCE) against a vulnerable SharePoint server. Today, both Rapid7 and Microsoft are disclosing the second vulnerability in this chain, the RCE …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Project CAV3RN continues: Google Apps Script as C2 relay and DNS-based C2 channel selection Moderate Kaspersky Securelist
2026-08-11 Kaspersky Securelist

Project CAV3RN continues: Google Apps Script as C2 relay and DNS-based C2 channel selection

Project CAV3RN is a modular espionage framework used against targets in Israel. This report expands on two earlier publications: the first was published in June 2026 as part of our Kaspersky Threat Intelligence Reporting service , and the second was published on Securelist the following month, further documenting the framework’s evolving architecture and C2 …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Good, the Bad and the Ugly in Cybersecurity – Week 32 Moderate SentinelOne Threat Labs
2026-08-07 SentinelOne Threat Labs

The Good, the Bad and the Ugly in Cybersecurity – Week 32

The Good | Snowflake Hacker Pleads Guilty as Ransom Cartel Creator Draws 16 Years Connor Riley Moucka pleaded guilty in Seattle federal court this week to computer fraud, wire fraud, aggravated identity theft and conspiracy over the 2024 breaches of Snowflake customer accounts. The intrusions reached at least 165 organizations and exposed records tied to at …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification