Threat Wire
BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys BleepingComputer [Critical] FBI links $6.3 billion Binance crypto heist to North Korean hackers BleepingComputer [Critical] Alpine Linux rebuilds GitLab after attempted RCE attack CVE-2026-118539 [Critical] Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION CVE-2026-58882 [Critical] SMS of Death: Android under attack, an invisible SMS can block calls and emergency services The Hacker News [Critical] CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key The Hacker News [Critical] FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist CVE-2026-111357 [Critical] U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog BleepingComputer [Critical] Northflank security breach leads to abuse of customers' AI API keys

CyberWatch Newsroom Live Intel

Continuous enterprise threat intelligence tracking active in-the-wild zero-days (CISA KEV), Microsoft Windows KB cumulative updates, MSRC security advisories, and CVE remediation.

Last Checked: Nov 2, 2026 - 02:28:59 UTC (Hourly Auto-Sync Active)
Showing 24 of 608 advisories
Page 15 of 26
From Input to Impact: Secure AI Where It Runs Moderate SentinelOne Threat Labs
2026-08-04 SentinelOne Threat Labs

From Input to Impact: Secure AI Where It Runs

AI agents have made their way into virtually every layer of your environment. They run in the apps your employees adopt, on the endpoints where agents execute code, as users with access privileges those agents borrow, and in the cloud workloads that scale them. The platform that you trust to secure your endpoints is already already covering where AI operates…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.

3rd August – Threat Intelligence Report Moderate CVE-2026-59726 Check Point Research
2026-08-03 Check Point Research

3rd August – Threat Intelligence Report

For the latest discoveries in cyber research for the week of 27th July, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Minnesota IT Services has confirmed coordinated cyberattacks affecting more than 30 community water utilities across the state. The incidents briefly disrupted a treatment plant in Braham and affected industrial c…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Good, the Bad and the Ugly in Cybersecurity – Week 31 Moderate SentinelOne Threat Labs
2026-07-31 SentinelOne Threat Labs

The Good, the Bad and the Ugly in Cybersecurity – Week 31

The Good | Authorities Disrupt “The Com”, Release Security Guidelines & Charge Telegram CEO Europol and law enforcement partners from nine countries have flagged over 4000 URLs for removal to disrupt the online ecosystem of The Com . Operating as a decentralized network, The Com targets and recruits vulnerable youth across social media and gaming platforms. …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Good, the Bad and the Ugly in Cybersecurity – Week 30 Moderate SentinelOne Threat Labs
2026-07-24 SentinelOne Threat Labs

The Good, the Bad and the Ugly in Cybersecurity – Week 30

The Good | Authorities Dismantle Kratos Phishing Network & Arrest Its Developer Kratos, a prominent phishing-as-a-service (PhaaS) platform, was dismantled from the inside out this week thanks to German and U.S. law enforcement agencies. During “Operation Olympus Blade”, authorities seized over 200 servers to render Kratos’ global network entirely inoperable …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Pwn2Own Ireland 2026 – New Targets and Categories Critical Trend Micro ZDI
2026-07-21 Trend Micro ZDI

Pwn2Own Ireland 2026 – New Targets and Categories

If you just want to read the rules, you can find them here . Pwn2Own Ireland returns for 2026, and it’s the third year for this event in the Emerald Isle. Despite the dreary Irish skies (and the threat of a random banshee ), we had an amazing event, even if we did end up in a jail at the end. With that in mind, we’re excited to return to Cork this fall for y…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The July 2026 Security Update Review Critical CVE-2026-56155 Trend Micro ZDI
2026-07-14 Trend Micro ZDI

The July 2026 Security Update Review

Well folks. Here we are. The bug apocalypse has fully descended upon us. I’ll do my best to sort this out in some way meaningful, but this month’s release shows us the nay-sayers were right, and I’ve got to hand it to the nay-sayers here. Excellent call. Take an extended break from your regularly scheduled activities as we let’s take a look at the latest sec…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
How GitHub gave every repository a durable owner Moderate GitHub Security Blog
2026-07-09 GitHub Security Blog

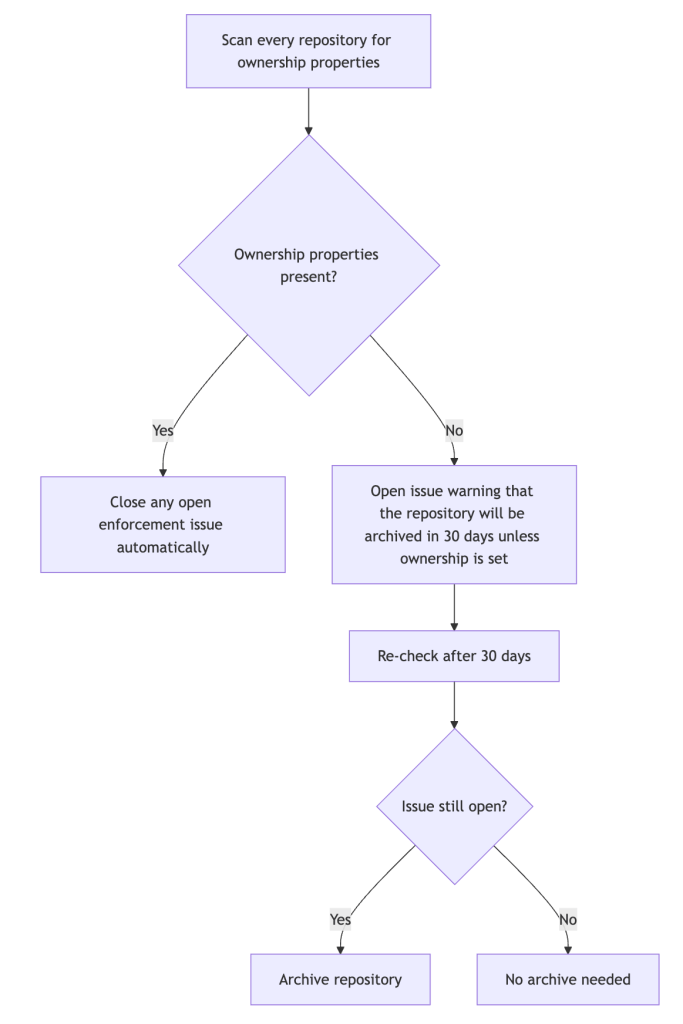
How GitHub gave every repository a durable owner

GitHub has over 14,000 repositories across our primary internal GitHub organization. As of early 2025, there were over 11,000 non-archived repositories, the vast majority of which with no clear owner. For repositories attached to production services, we have historically had robust durable ownership, but for repositories with no associated service, there was…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The June 2026 Security Update Review Critical CVE-2026-41091 Trend Micro ZDI
2026-06-09 Trend Micro ZDI

The June 2026 Security Update Review

I’ve made it through Pwn2Own Berlin, had a little vacation, and now I’m back for Patch Tuesday. Microsoft and Adobe didn’t disappoint. In fact, they have heralded my return with the largest Patch Tuesday release ever. Thanks? Take a break from your regularly scheduled activities and let’s take a look at the latest security patches from Adobe and Microsoft. I…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Defend against frontier cyber models: Cloudflare's architecture as customer zero Moderate Cloudflare Security
2026-06-09 Cloudflare Security

Defend against frontier cyber models: Cloudflare's architecture as customer zero

A few weeks ago, we wrote about Project Glasswing and what we observed when we pointed cyber frontier models at our own code. Since then, we’ve seen that the part of the post that has resonated most deeply is the argument that the architecture around the vulnerability matters more than the speed of the patch. In the conversations we've had with CISOs and sec…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Pwn2Own Berlin 2026: Day Three Results and Master of Pw Critical Trend Micro ZDI
2026-05-16 Trend Micro ZDI

Pwn2Own Berlin 2026: Day Three Results and Master of Pw

Following two days of intense competition, Day Three of Pwn2Own Berlin 2026 brought the curtain down on an incredible event. Security researchers delivered their final exploits, pushing enterprise systems to the limit one last time as the race for Master of Pwn came to a close. Day Three added to an already historic event, bringing the final totals to $1,298…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Pwn2Own Berlin 2026 - Day Two Results Critical Trend Micro ZDI
2026-05-15 Trend Micro ZDI

Pwn2Own Berlin 2026 - Day Two Results

Day Two of Pwn2Own Berlin 2026 and the stakes continue to rise! Security researchers are back on the Pwn2Own stage, pushing enterprise systems to their limits as the competition heats up. More exploits, more surprises, and more standout moments are unfolding, so follow along here for live updates as the race for Master of Pwn intensifies. There were plenty o…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Pwn2Own Berlin 2026 - Day One Results Critical Trend Micro ZDI
2026-05-14 Trend Micro ZDI

Pwn2Own Berlin 2026 - Day One Results

Welcome to Day One of Pwn2Own Berlin 2026! Today, 22 entries took the Pwn2Own stage to target AI Databases, Coding Agents, Local Inferences, and a separate category for NVIDIA products, as the world’s top security researchers push technology to its limits. Exploits, surprises, and breakthrough discoveries are unfolding. After Day One, we awarded $523,000 for…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The May 2026 Security Update Review Critical CVE-2026-41096 Trend Micro ZDI
2026-05-12 Trend Micro ZDI

The May 2026 Security Update Review

I’m currently in Berlin helping set up for Pwn2Own Berlin, but that doesn’t stop Patch Tuesday from coming, and it’s another big one. At least nothing is listed as being in the wild – for now. Take a break from your regularly scheduled activities and let’s take a look at the latest security patches from Adobe and Microsoft. Due to technical difficulties, the…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The Apple macOS Security Update Review Moderate CVE-2026-28819 Trend Micro ZDI
2026-05-12 Trend Micro ZDI

The Apple macOS Security Update Review

We’ve received some feedback from those who read the Patch Blog that they would like something similar for macOS updates. Unfortunately, Apple doesn’t schedule these for a particular day, but we can provide our thoughts and analysis on the days they do release their latest patches. For May 2026, Apple released 82 unique CVEs across the three macOS versions: …

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
AI threats in the wild: The current state of prompt injections on the web Critical Google Online Security
2026-04-23 Google Online Security

AI threats in the wild: The current state of prompt injections on the web

Posted by Thomas Brunner, Yu-Han Liu, Moni Pande At Google, our Threat Intelligence teams are dedicated to staying ahead of real-world adversarial activity, proactively monitoring emerging threats before they can impact users. Right now, Indirect Prompt Injection (IPI) is a top priority for the security community, anticipating it as a primary attack vector f…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The April 2026 Security Update Review Critical CVE-2026-32201 Trend Micro ZDI
2026-04-14 Trend Micro ZDI

The April 2026 Security Update Review

It’s time once again for Patch Tuesday, and this one is huge. We’ve also got multiple exploits in the wild, which adds another layer of urgency to this month’s release. Take a break from your regularly scheduled activities, and let’s take a look at the latest security patches from Adobe and Microsoft. If you’d rather watch the full video recap covering the e…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Node.js Trust Falls: Dangerous Module Resolution on Windows Critical CVE-2026-0776 Trend Micro ZDI
2026-04-08 Trend Micro ZDI

Node.js Trust Falls: Dangerous Module Resolution on Windows

In September of 2024, ZDI received a vulnerability submission from an anonymous researcher affecting npm CLI that revealed a fundamental design issue in Node.js . This blog details how it continues to expose applications to local privilege escalation (LPE) attacks on Windows systems, including the Discord desktop app (CVE-2026-0776 0-Day), which remains unpa…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Cloudflare Client-Side Security: smarter detection, now open to everyone Moderate Cloudflare Security
2026-03-30 Cloudflare Security

Cloudflare Client-Side Security: smarter detection, now open to everyone

Client-side skimming attacks have a boring superpower: they can steal data without breaking anything. The page still loads. Checkout still completes. All it needs is just one malicious script tag. If that sounds abstract, here are two recent examples of such skimming attacks: In January 2026, Sansec reported a browser-side keylogger running on an employee me…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Announcing Pwn2Own Berlin for 2026 Moderate Trend Micro ZDI
2026-03-12 Trend Micro ZDI

Announcing Pwn2Own Berlin for 2026

If you just want to read the contest rules, click here . Willkommen zurück, meine Damen und Herren, zu unserem zweiten Wettbewerb in Berlin! That’s correct (if Google translate didn’t steer me wrong). After our inaugural competition last year, Pwn2Own returns to Berlin and OffensiveCon . Outside of our shipping troubles , we had an amazing time and can’t wai…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
The March 2026 Security Update Review Moderate CVE-2026-26144 Trend Micro ZDI
2026-03-10 Trend Micro ZDI

The March 2026 Security Update Review

I am back in the friendly confines of the Mid-South headquarters of TrendAI ZDI (a.k.a. my home office), and am all set for the third patch Tuesday of 2026. Take a break from your regularly scheduled activities and let’s take a look at the latest security patches from Adobe and Microsoft.If you’d rather watch the full video recap covering the entire release,…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Rust in Android: move fast and fix things Critical CVE-2025-48530 Google Online Security
2025-11-13 Google Online Security

Rust in Android: move fast and fix things

Posted by Jeff Vander Stoep, Android Last year, we wrote about why a memory safety strategy that focuses on vulnerability prevention in new code quickly yields durable and compounding gains. This year we look at how this approach isn’t just fixing things, but helping us move faster . The 2025 data continues to validate the approach, with memory safety vulner…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
HTTPS by default Critical Google Online Security
2025-10-28 Google Online Security

HTTPS by default

One year from now, with the release of Chrome 154 in October 2026, we will change the default settings of Chrome to enable “Always Use Secure Connections”. This means Chrome will ask for the user's permission before the first access to any public site without HTTPS. The “Always Use Secure Connections” setting warns users before accessing a site without HTTPS…

Fix: Review advisory findings, isolate suspect endpoints, and verify threat signatures.
Notification